- ホーム
- CompTIA
- XK0-005-JPN - CompTIA Linux+ Certification Exam (XK0-005日本語版)
- CompTIA.XK0-005-JPN.v2026-01-07.q429
- 質問143
有効的なXK0-005-JPN問題集はJPNTest.com提供され、XK0-005-JPN試験に合格することに役に立ちます!JPNTest.comは今最新XK0-005-JPN試験問題集を提供します。JPNTest.com XK0-005-JPN試験問題集はもう更新されました。ここでXK0-005-JPN問題集のテストエンジンを手に入れます。
XK0-005-JPN問題集最新版のアクセス
「895問、30% ディスカウント、特別な割引コード:JPNshiken」
ユーザーから/mnt/dataディレクトリ内のファイルへのアクセスに関する問題が報告されました。Linux管理者がディレクトリの内容を調べたところ、以下の情報を発見しました。
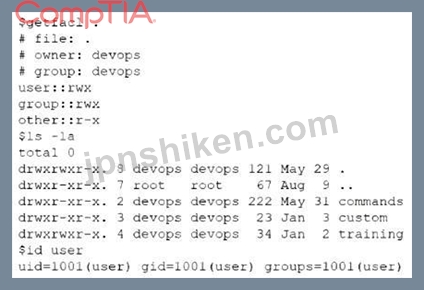
ユーザーの問題を解決するための最も安全な方法はどれですか?
ユーザーの問題を解決するための最も安全な方法はどれですか?
正解:B
The ACL shows only the default owner/group permissions and "other" is read-only. Granting the specific user read/write via an ACL entry (e.g. setfacl -m u:user:rwX /mnt/data) gives them the needed access without making the directory world-writable or changing ownership.

- 質問一覧「429問」
- 質問1 ジュニアシステム担当者がローカリゼーションオプションの環境変
- 質問2 Linux システム管理者は、ネットワーク構成ファイル内の IP アド...
- 質問3 システム管理者は、インターネットベースのリポジトリからサーバ
- 質問4 ユーザーから、MariaDBサービスへの接続が予期せず切断されると...
- 質問5 開発者がSSH経由でLinuxサーバーにアクセスできません。次のよう...
- 質問6 システム管理者は、永続的な IPv4 パケット転送を可能にするため...
- 質問7 Linux管理者が初めてサーバーにログインし、ファイアウォールを...
- 質問8 開発者がアプリケーション構成ファイルに関するインシデントを報
- 質問9 Linux管理者は、systemdタイマーが毎晩深夜に実行されない原因を...
- 質問10 Linux ユーザーがシステムにインストールされている PCI デバイ...
- 質問11 ユーザーが「developer」という名前のアカウントを使用して Linu...
- 質問12 Linuxシステム管理者は、APTを使用してアップデートをインストー...
- 質問13 システム管理者がコマンドラインからプログラムを起動した後、Ct...
- 質問14 技術者がユーザー名 Joe の管理者アカウントを作成するために使...
- 質問15 システム管理者は、Linuxシステムの1つで発生した問題に関する報...
- 質問16 Linuxシステムは、いくつかの重要なシステムプロセスに問題があ...
- 質問17 SysV init を実行しているシステムを、メンテナンス タスクを安...
- 質問18 新しい企業ポリシーでは、社内のすべてのラップトップで Bluetoo...
- 質問19 セキュリティアナリストは、脆弱性スキャン中に発生する遅延や速
- 質問20 Linux管理者はテスト環境を構築しており、本番サーバー名を使用...
- 質問21 Linux 管理者は、ボリューム グループに属するすべてのボリュー...
- 質問22 ユーザーから、Linuxサーバーにログインしようとした際に問題が...
- 質問23 Linux で Ctrl-Alt-Del を無効にするには、次のどの設定ファイル...
- 質問24 Linux管理者がサーバーを再起動したところ、ユーザーから一部の...
- 質問25 ユーザーは/app1マウントポイントに保存されているアプリケーシ...
- 質問26 システム管理者は、newmodカーネルモジュールを必要とする新しい...
- 質問27 システム管理者は、セキュリティ上の理由から、Linux カーネル W...
- 質問28 企業のサーバーセキュリティポリシーには、「パスワードハッシュ
- 質問29 ユーザーのジョーはLinuxシステムにログインできません。次のよ...
- 質問30 Linux管理者は、新しいディスクを使用してボリュームグループを...
- 質問31 システム管理者は、webというユーザーによって作成されたすべて...
- 質問32 管理者がリソースの観点から Linux サーバーの仕様を識別するの...
- 質問33 最近、Debian/UbuntuサーバーにApacheウェブサーバーをインスト...
- 質問34 システム管理者が手動で新しいライブラリをサーバーに追加しまし
- 質問35 システム管理者は、別のVLANからデータをコピーするために、新し...
- 質問36 Linux システム管理者が新しい Web サーバーをインストールしま...
- 質問37 管理者は、Linuxワークステーションがウェブサイトを解決できな...
- 質問38 システム管理者は、foo.com ドメインのメール交換 (MX) レコード...
- 質問39 管理者はmyhost上のSSHサーバーにポート2222を追加し、SSHサーバ...
- 質問40 ジュニアシステム管理者が、ウイルス対策スキャナーを使用して a...
- 質問41 管理者は、実行状態に関係なく、現在稼働中のすべてのコンテナを
- 質問42 Linux管理者は、仮想サーバーにI/Oボトルネックが発生しているこ...
- 質問43 システムエンジニアが新しいアプリケーションサーバーを導入しま
- 質問44 Linux管理者は、ホスト名がDNSに登録されているかどうかを確認す...
- 質問45 アプリケーションチームは、/appfile システム内のデータにアク...
- 質問46 ユーザー1は会計グループのメンバーです。このグループのメンバ
- 質問47 Linux 管理者は、パブリック クラウド プロバイダーを使用して、...
- 質問48 管理者は、SSH 認証用のキーをリモート サーバーのホーム ディレ...
- 質問49 空きディスク容量が十分であるにもかかわらず、再起動後に syste...
- 質問50 サーバーの1つを強化するために、管理者はSSHサービス経由のリモ...
- 質問51 ユーザーはドキュメントを /home/tmp/temp に保存できず、次のエ...
- 質問52 システム管理者は、ファイルの種類とファイルの内容に関する情報
- 質問53 開発者が、チームで使用しなくなった特定のデータフォルダを削除
- 質問54 初心者のLinux管理者がアプリケーションのインストールを任され...
- 質問55 システム管理者は、ソフトウェアRAIDを使用してLinuxサーバーの...
- 質問56 Linux ストレージ管理者は論理ボリューム グループを作成したい...
- 質問57 あるファイルサーバーが、社内のチームメンバー間で/shareという...
- 質問58 システム管理者は、3 時間前にバックグラウンドで開始された一連...
- 質問59 オペレーターは、ユーザーが特定のファイルを開く際に問題を抱え
- 質問60 YAML と JSON の違いは次のどれですか?
- 質問61 システム管理者は、ext4ファイルシステム形式のUSBストレージデ...
- 質問62 ユーザーのジョーから、ホームディレクトリにファイルを書き込め
- 質問63 ユーザーがサーバーにリモートでログインしようとすると、次のメ
- 質問64 Linux管理者がサーバー上でSSH経由のルートログインを有効にしよ...
- 質問65 Linux管理者は、エンドユーザーが社内クラウドサーバーにアクセ...
- 質問66 Linux管理者は、新しくインストールされたアプリケーションを監...
- 質問67 Linux システム管理者は、再起動後も永続的にマウントできる機能...
- 質問68 Linux管理者は、大規模なアプリケーションサービスをコンテナ化...
- 質問69 経験の浅いシステム管理者が、本番環境に導入されているサーバー
- 質問70 経験の浅いLinux管理者がSSHサーバーを設定しており、デフォルト...
- 質問71 Linux 管理者が Java アプリケーションを実行するスクリプトを実...
- 質問72 システム管理者が/etc/passwdファイルの権限を変更しました。ユ...
- 質問73 Linux管理者は、システムタイマーが毎晩午前0時に実行されない原...
- 質問74 ある企業の社内ユーザーから、ウェブサイトの応答速度が遅いとい
- 質問75 管理者は、静的に割り当てられたワークステーションのグループが
- 質問76 Linux管理者がLinuxサーバーでKVMの使用を開始しようとしていま...
- 質問77 ログイン管理にデータベースを使用するウェブアプリケーションで
- 質問78 Linux 管理者は、Linux サーバー上の Sendmail サービスを無効に...
- 質問79 システム管理者は、スペースを節約するために古いログファイルを
- 質問80 ある企業では、新しく作成されたすべてのファイルはその所有者だ
- 質問81 Linux管理者は、監査要件を満たすために、Linuxサーバーへのルー...
- 質問82 次のデータ構造のうち、JSON で記述されているものはどれですか?...
- 質問83 lspci コマンドは、システム ハードウェアについてどのような情...
- 質問84 SSDドライブを搭載したシステムで、書き込みに予想以上に時間が...
- 質問85 Linux 管理者は、本番環境で高可用性、移植性、およびスケーラビ...
- 質問86 次のサーバー ロールのうち、ホスト IP アドレスを割り当てるの...
- 質問87 Linux管理者は、ディスクの空き容量を1時間ごとに確認するスクリ...
- 質問88 Linux管理者がシステム全体のSELinuxコンテキストを復元しようと...
- 質問89 Linux管理者は、リモートサーバーのポート8000をローカルサ...
- 質問90 セキュリティ チームは、特定のサーバーがオープン リレーとして...
- 質問91 システム管理者は、リモート Web サーバーにアクセスするときに...
- 質問92 データベース管理者が、サーバーの 1 つにカスタム データベース...
- 質問93 Linux管理者がシステムで作業中に、一部のパッケージが最新バー...
- 質問94 システム管理者が myfile ファイルのファイル権限を変更しました...
- 質問95 システム管理者が ~/.bashrc ファイルにいくつかの変更を加え、...
- 質問96 Linux管理者は、システムにユーザーを追加する任務を負っていま...
- 質問97 SysV init を使用しているときにシステムを再起動するコマンドは...
- 質問98 システム管理者は、Linux サーバーのネットワーク ポートをリッ...
- 質問99 Linux 管理者は、コンテナ内で実行されている障害のあるアプリケ...
- 質問100 システム管理者は、論理ボリューム /dev/mapper/linux-root を拡...
- 質問101 Linux管理者は、既存のACLを使用せずに新しいファイアウォールを...
- 質問102 Linux管理者が、社内会計WebアプリケーションにCI/CDプロセスを...
- 質問103 ユーザー(userA)がシステムへのログイン中に問題を報告しまし...
- 質問104 Linux管理者がCompTIA_docというディレクトリを作成しようとして...
- 質問105 システム管理者は、実行中の systemd サービス tor を停止し、シ...
- 質問106 Kerberos SSOが有効になっているLinuxサーバーにユーザーがログ...
- 質問107 Linux 管理者は /usr/domain フォルダーをバックアップする必要...
- 質問108 Linux管理者は、ファイルサイズが大きくなるにつれてデータが追...
- 質問109 Linuxシステム管理者は、Linuxサーバーのネットワークインターフ...
- 質問110 管理者がマスターオンラインGitリポジトリの更新を確認している...
- 質問111 Linux管理者は、ユーザーがアクセスできない問題をトラブルシュ...
- 質問112 複数のユーザーから、/oracle1ディレクトリにデータを書き込めな...
- 質問113 ユーザーがSSH経由で仮想サーバーへのアクセス要求を送信します...
- 質問114 管理者は現在のストレージを拡張するために新しいディスクを追加
- 質問115 管理者は、/opt/tools からホームディレクトリ /home/admin にフ...
- 質問116 journald のエントリが Linux マシンの /var ボリュームをいっぱ...
- 質問117 システム管理者は、installer_0.17-41.2_amd64.deb ファイルをイ...
- 質問118 サードパーティのソフトウェアをインストールする際に、技術者は
- 質問119 AD クエリを使用する場合、セキュリティ ゲートウェイはどのプロ...
- 質問120 複数のドライブが同時に故障した場合に、データ損失を大幅に削減
- 質問121 人事部門のユーザーは、新しく作成されたディレクトリ内のファイ
- 質問122 管理者は SSH 経由でクラウド内のサーバーにアクセスしようとし...
- 質問123 Linux 管理者の Ann は、スクリプトをプライベート Git リポジト...
- 質問124 grub.cfg ファイルのテンプレートは次のどれですか?
- 質問125 Linux管理者がデフォルトのシステムumaskを変更しようとしていま...
- 質問126 Linux 管理者は最近、従来の Web サーバーを置き換えるために新...
- 質問127 システム管理者は、サーバーのシステムアップデートをスケジュー
- 質問128 システム管理者はシステムパーティション /dev/sda1 を /dev/sdc...
- 質問129 サーバーで断続的な接続問題が発生しています。インターネットへ
- 質問130 管理者は、長時間実行されるスクリプト /home/user/script.sh が...
- 質問131 制作グループのメンバーが次のコマンドを発行します。 echo "月...
- 質問132 システム管理者は、複数のプロセスがゾンビ状態にあることを発見
- 質問133 次のディレクトリのうち、UEFI システムのマウント ポイントはど...
- 質問134 ネットワーク管理者がdig www.foo.comコマンドを発行し、NXDOMAI...
- 質問135 Linux 管理者は、Linux サーバーに新しいローカル ユーザーが作...
- 質問136 シミュレーション ログインのログ ファイルを解析して、誰がいつ...
- 質問137 Linux 管理者が httpd パッケージをダウンロードしてインストー...
- 質問138 エンジニアは、viテキストエディタで現在の行の末尾に文字を挿入...
- 質問139 システム管理者は、太平洋タイム ゾーンに展開される新しくイン
- 質問140 システム管理者は、計画されたシステム再起動後にWebサーバーが...
- 質問141 Linux システムが次のエラーで起動に失敗します。 (Exhibit) こ...
- 質問142 Linux管理者は新しいDNSフォワーダーを設定し、すべての内部サー...
- 質問143 ユーザーから/mnt/dataディレクトリ内のファイルへのアクセスに...
- 質問144 システム管理者が社内Wikiに、自社のコードをDebianパッケージに...
- 質問145 サーバーに新しいデータベースがインストールされます。データベ
- 質問146 管理者は、Linux サーバーにインストールされているメモリの量を...
- 質問147 仮想化環境のストレージ管理者は、ユーザーからボリュームに書き
- 質問148 管理者が SSH 経由でリモート ホストに接続した後、アプリケーシ...
- 質問149 udev を使用する場合の /dev/ に関して、次の記述のうち正しいも...
- 質問150 Linux管理者がパッケージマネージャーを使用してパッケージ newp...
- 質問151 テクニカルサポートエンジニアは、1KBのファイルを作成しようと...
- 質問152 vi でファイルを編集しているときに、/dev/sdc のすべての出現を...
- 質問153 Linux エンジニアは、PID 7991 の oom_score 値を決定する必要が...
- 質問154 Linuxシステム管理者がサーバー上で特定のシェルスクリプトを実...
- 質問155 Linux管理者は、特定のマウントポイントやディレクトリが指定さ...
- 質問156 管理者は「web」というコンテナでWebサーバーを実行していますが...
- 質問157 管理者が誤って、httpd RPM パッケージをいくつかの依存関係とと...
- 質問158 Linux管理者は、現在のディレクトリにあるすべてのファイルを含...
- 質問159 Linux管理者はサーバーを再起動し、現在サーバーに接続している...
- 質問160 システム管理者は、/var/log/appディレクトリ内のすべてのアプリ...
- 質問161 管理者が誤って /boot/vmlinuz ファイルを削除したため、サーバ...
- 質問162 SysV init を使用する場合、通常、ブート時に Linux カーネルに...
- 質問163 新しく採用されたジュニア管理者が/var/log/messagesファイルの...
- 質問164 Linux 管理者は、権限のないユーザーがリモートから Linux サー...
- 質問165 システム管理者は、.tar.bz2 形式を使用してログファイルを圧縮...
- 質問166 ネットワーク管理者がdig www.comptia.orgコマンドを発行し...
- 質問167 システム管理者はLinuxサーバーの/homeディレクトリでクォータを...
- 質問168 システム管理者は、UID が 500 より大きいすべてのローカル アカ...
- 質問169 システム管理エンジニアは、LinuxサーバーのタイムゾーンをAmeri...
- 質問170 管理者が新しいカーネルをインストールしようとしたところ、ファ
- 質問171 Linuxシステムに問題が発生しています。以下の出力が表示されま...
- 質問172 管理者が最初のGitリポジトリを作成し、最初のファイルをアップ...
- 質問173 ユーザーは、サーバー名 server1 とポート 22 を使用してサーバ...
- 質問174 Linux管理者は、最終的な設定情報を入力するのにデスクトップWeb...
- 質問175 システム管理者は次のコードを使用して Web サーバーを展開して...
- 質問176 Linux管理者が既存のLinuxサーバーのクローンを作成し、そのクロ...
- 質問177 管理者がサーバー上のファイルの名前を変更しようとしましたが、
- 質問178 Linux 管理者は、停止されているコンテナも含め、すべてのコンテ...
- 質問179 堅牢なアプライアンスは、堅牢なハードウェアを備えた小型アプラ
- 質問180 技術者がコードのいくつかの問題を修正し、コードを本番環境に展
- 質問181 シミュレーション 上級管理者がユーザー admin の秘密鍵をホーム...
- 質問182 システム管理者は、新しいドライバーを必要とする新しいハードウ
- 質問183 管理者は、すべてのユーザーがそのコンテンツに書き込み、実行で
- 質問184 管理者は、最近侵害を受けた Linux システムを検査しているとき...
- 質問185 内部証明機関 (ICA) はどの時点で作成されますか?
- 質問186 組織は、ユーザー情報全体を集中ストレージに統合したいと考えて
- 質問187 Linux システムでディスク暗号化を実行するために使用される仕様...
- 質問188 ユーザーは次のコマンドを発行します。 ls -l /var/log | egrep ...
- 質問189 システム管理者は、内部ネットワーク172.17.0.0/16からeth0イン...
- 質問190 上級Linux管理者が、一般的なシステムアプリケーションのインス...
- 質問191 Linuxエンジニアが以前作成したファイアウォールルールを削除し...
- 質問192 Linux管理者は、ネットワーク運用チームから、Linuxサーバー上の...
- 質問193 ユーザーから、同社のウェブサイト(https://www.comptia.org)...
- 質問194 新しく作成されたコンテナが正常に起動できず、Linux 管理者が失...
- 質問195 システム管理者が「test」という新しいDockerイメージを作成しま...
- 質問196 Linux 管理者は、CPU 負荷と平均値が高くなる根本原因をトラブル...
- 質問197 セキュリティ チームは、昇格された権限で実行されている Web サ...
- 質問198 Linux管理者は、サーバーのタイムゾーンが正しくないことを知ら...
- 質問199 ある初心者のLinux管理者が、IPv6をサポートするためにローカル...
- 質問200 ユーザー jsmith は、サーバー上にあるデータベース ファイルに...
- 質問201 組織の新しいサイバーセキュリティ ポリシーに基づいて、管理者
- 質問202 Linux管理者は、すべてのHTTPトラフィックを一時的に新しいプロ...
- 質問203 ある組織の事業部は四半期報告書の作成に協力する必要があり、シ
- 質問204 管理者は、ターミナルでフォアグラウンド プロセスの実行中にそ
- 質問205 Linux システム管理者は、サーバー A からサーバー B にファイル...
- 質問206 ユーザーは /mnt/storage にある NFS データストアにデータを書...
- 質問207 新しい HTTPS Web サービスがサーバーに展開されています。 トラ...
- 質問208 システム管理者は、db.example.comというシステムへのアクセスに...
- 質問209 Linuxシステム管理者は、管理者グループのメンバーであるユーザ...
- 質問210 システム管理者は、ポートで実行されているアプリケーションへの
- 質問211 システム技術者が、IPアドレス192.168.10.22を持つ信頼できるソ...
- 質問212 開発者は、共有フォルダ内に作成されたすべてのファイルとフォル
- 質問213 システム管理者は、パブリックプロバイダー向けに一連のUbuntuイ...
- 質問214 管理者はWEBというコンテナでWebサーバーを実行していますが、エ...
- 質問215 Linux 管理者は、起動時に Postfix メール転送エージェントが起...
- 質問216 システム管理者は、Linuxシステムに関する問題に関する報告を受...
- 質問217 システム管理者は Linux サーバーにログインし、サーバーが物理...
- 質問218 複数のサービスがクラッシュした場合、管理者はサービスがクラッ
- 質問219 管理者は、NTP サーバーへのネットワーク接続がない VM の時刻を...
- 質問220 システム管理者は接続の問題をトラブルシューティングし、Linux ...
- 質問221 ジュニア システム管理者の Ann は、/etc/yum.conf ファイルに 1...
- 質問222 ユーザーは、システムの起動時に毎回、アプリケーション「myapp...
- 質問223 Linux管理者はサーバーの権限を設定する必要があります。管理者...
- 質問224 Linux 管理者は、systemd を使用してシステムを再起動する前に、...
- 質問225 システム管理者がユーザーの資格情報の変更要求を受け取りました
- 質問226 システム管理者は、パスワードで保護されたSSHキーを利用して、...
- 質問227 シミュレーション 新しい Web サーバーをインストールした後、デ...
- 質問228 新しい Linux ハードウェアのステージングの最終ステップで、GRU...
- 質問229 システム管理者は、現在のアプリケーション サーバー上のファイ
- 質問230 Linux管理者が共有ターミナル上でリモートホストへの接続をテス...
- 質問231 ドラッグアンドドロップの質問 リードLinuxは、ディスク容量が不...
- 質問232 管理者がソースから/opt/operations1/にアプリケーションをイン...
- 質問233 サーバー上でホストされている Web サイトにアクセスしようとす...
- 質問234 Linux管理者は、サーバーに現在インストールされているパッケー...
- 質問235 システム管理者はfirewalldを使用してファイアウォールルールを...
- 質問236 Linux 管理者は、デフォルト設定を使用して新しい HTTP サーバー...
- 質問237 次のコマンドのうちどれがオペレーティング システムを表示しま
- 質問238 ログインする際、管理者はキーフォブに表示される 6 桁の一時コ...
- 質問239 Linux サーバーへの非ルート SSH アクセスを防ぐのは次のどれで...
- 質問240 システム管理者はarchive.tar.xzの内容を一覧表示する必要があり...
- 質問241 管理者はリモートサーバーにアクセスできるようにしたいと考えて
- 質問242 Linux システム管理者が新しい Web サーバーをセットアップして...
- 質問243 Linuxシステムユーザーから、ここ数ヶ月、サーバーが1日に少なく...
- 質問244 アプリケーションでは、アカウント作成時に各ユーザーのホームデ
- 質問245 システム管理者は、パッケージの新しいバージョンをインストール
- 質問246 開発者は、Nginxイメージコンテナを起動し、Web00lという名前を...
- 質問247 Linuxエンジニアが、ユーザーOliverにcloud_usersディレクトリの...
- 質問248 サーバー管理者には、すべてのサーバー間で同期する必要があるア
- 質問249 システム管理者は、システムアカウントのプロパティを一覧表示し
- 質問250 Linux管理者のアンは、設定管理ファイルを編集したいと考えてい...
- 質問251 システム管理者はLinuxラップトップを使用してネットワークデバ...
- 質問252 システム管理者は、会社の内部データベース レコードを更新する
- 質問253 システム管理者はシステムログをチェックしています。管理者は最
- 質問254 システム管理者は、LinuxサーバーがインターネットホストからのH...
- 質問255 管理者は権限のないユーザーとしてログオンし、ソースからアプリ
- 質問256 初級システム管理者がマウントポイント /data を持つ新しいファ...
- 質問257 ユーザーから、Webサーバーへの安全な接続時に問題が発生したと...
- 質問258 Linux サーバーへの非ルート SSH アクセスを防ぐのは次のどれで...
- 質問259 Linux システムからクラウド プロバイダーで実行されている Wind...
- 質問260 仮想プライベート クラウドに展開されているアプリケーションの
- 質問261 システム管理者は、リポジトリからコードをチェックアウトし、新
- 質問262 Linux管理者がローカルのラップトップで新しいWebアプリケーショ...
- 質問263 Linux管理者がシステムに新しいRAIDアダプタを物理的に追加しま...
- 質問264 システム ログが一般的に保存されるファイル システムは次のうち...
- 質問265 Linux管理者がネットワークトラフィック転送を設定しています。...
- 質問266 システム管理者は、起動しないサービスを調査しています。以下の
- 質問267 ジュニア システム管理者が DNS サーバーの設定を確認するために...
- 質問268 経験の浅いシステム管理者が、Red Hat ベースのシステムにインス...
- 質問269 システム管理者がSFTPサーバーの設定作業を行っています。10.10....
- 質問270 Linux管理者は、sdaディスクからsda.imgというイメージを作成し...
- 質問271 システム管理者は、CSVファイルから特定のフィールドを取得する...
- 質問272 管理者がApacheウェブサーバーをプロビジョニングしています。管...
- 質問273 UEFI ベースのシステムでは、次のどれが EFI コマンド プロンプ...
- 質問274 システム管理者は、システムにUSBドライブをマウントする任務を...
- 質問275 次のディレクトリのうち、ルート ユーザーのみが実行できるバイ
- 質問276 ある企業が、ネットワークに接続されたデバイス向けに社内ID認証...
- 質問277 /bin/passwdfile に SUID 権限が設定されている理由を最もよく説...
- 質問278 サービス メッシュの利点は次のどれですか?
- 質問279 JSON を最もよく表すのは次のどれですか?
- 質問280 経験の浅いシステム管理者がcronジョブを作成しています。cronジ...
- 質問281 Linux管理者がLinuxサーバーにステートフルファイアウォールを実...
- 質問282 新しいファイルのデフォルトの権限を構成するために使用されるコ
- 質問283 初心者のLinux管理者であるアンは、IPアドレス192.168.3.22を持...
- 質問284 ユーザーは、実際のメッセージからダッシュのセットで区切られた
- 質問285 Linux 管理者がローカル ディスクではなくネットワーク インター...
- 質問286 管理者は構成管理ツールを使用してシステムの構成を定義していま
- 質問287 システム管理者は、SSH と非標準ポートを介してリモート ホスト...
- 質問288 Linux管理者は、Linuxシステム上のすべてのローカルファイアウォ...
- 質問289 Linuxエンジニアは、foo.comドメインのメールサーバーから情報を...
- 質問290 Linux管理者は、システムを強化し、再起動やシステムアップグレ...
- 質問291 システム管理者がSSH経由でサーバーにアクセスしようとしていま...
- 質問292 サーバーのIPアドレスが10.115.6.5から10.116.6.5に変更されまし...
- 質問293 ユーザーは/home/userディレクトリにファイルを書き込むことがで...
- 質問294 Linuxエンジニアは、IPアドレス2.2.2.2からセキュアシェルサーバ...
- 質問295 Linux システム管理者は、ローカルの作業システム上の「working...
- 質問296 管理者は、特定のサーバーでバックアップが失敗する原因を特定す
- 質問297 Linux システム管理者は、サーバーのファイルシステムの 1 つが...
- 質問298 システムのブート サイクル中に、BIOS がタスクを完了した後に実...
- 質問299 システム管理者は認証用の公開鍵を作成します。リモートサーバー
- 質問300 リモートシステムへのSSHアクセスをリクエストした際、ユーザー...
- 質問301 システム管理者は、サードパーティベンダーのオフサイトに保存さ
- 質問302 次のオプションのうち、YAML の目的を説明しているものはどれで...
- 質問303 Linux 管理者は、ファイルを削除しようとしたときに次のメッセー...
- 質問304 セキュリティチームは、昇格された権限で実行されているWebサー...
- 質問305 タイプ 2 ハイパーバイザーについて正しいのは次のうちどれです...
- 質問306 最近、技術者がデスクトップ コンピュータに Linux をインストー...
- 質問307 システム管理者は、グラフィカルインターフェースからシステムア
- 質問308 あるエンジニアが、本番環境へのアプリケーションのデプロイ作業
- 質問309 システム管理者は、一般的な仮想化ソフトウェアをインストールし
- 質問310 X11 システムの目的を最もよく表しているのは次のうちどれですか...
- 質問311 SSH 認証中にユーザーの公開鍵がどのように使用されるかを説明し...
- 質問312 Linux管理者が、Ubuntuシステム上のソフトウェアおよびアップデ...
- 質問313 セキュリティポリシーにより、データベースサーバーへの直接アク
- 質問314 ユーザーは、Windows ワークステーションからターミナル サービ...
- 質問315 新しい Linux システム管理者が、サーバーへの接続を許可する SS...
- 質問316 サーバーの空きメモリがほとんどなくなり、応答しなくなっていま
- 質問317 システム管理者は、IPアドレスでの断続的なネットワーク接続のト...
- 質問318 Linux管理者は、Linuxシステムのネットワークインターフェースに...
- 質問319 Linux サーバーへの非ルート SSH アクセスを防ぐのは次のどれで...
- 質問320 毎分実行される構成管理ツールが、サービス HTTPd の起動を強制...
- 質問321 システム管理者がプロセスを終了できませんでした。管理者がプロ
- 質問322 Linux管理者が、会計ユーザー用の新しいsudoプロファイルを作成...
- 質問323 アプリケーションでは、アカウント作成時に各ユーザーのホームデ
- 質問324 システム管理者がLinuxサーバーに新しいソフトウェアプログラム...
- 質問325 Linux管理者は、毎週金曜日の午前2時15分にバックアップジョブを...
- 質問326 管理者は、システム ユーザーの暗号化されたパスワードのリスト
- 質問327 システム管理者はサーバーのメンテナンスを行う必要があります。
- 質問328 財務部門の従業員がファイル/opt/work/fileにアクセスできない問...
- 質問329 管理者はUSBドライブを受け取り、作業を開始する前にディスクの...
- 質問330 システム管理者はLinuxサーバーからディスクを取り外す必要があ...
- 質問331 Linux システムのデフォルト プリンタを表示するコマンドはどれ...
- 質問332 Linux管理者がアプリケーションサーバーの交換用ハードドライブ...
- 質問333 Linux エンジニアはシステムから次の通知を受け取ります。 cp: ...
- 質問334 Linux サーバーは Kerberos と LDAP をホストしますが、このサー...
- 質問335 システム管理者は、特定のウェブサイトへのネットワーク接続が断
- 質問336 管理者は新しいLinuxマシンをインストールするために、起動可能...
- 質問337 ある初心者のLinux管理者が、あるアプリケーションがプロセス実...
- 質問338 Linuxエンジニアは、特定のグループ内で作成されたファイルが、...
- 質問339 システム管理者は、ファイアウォールレベルでセキュアWebサービ...
- 質問340 システム管理者は、ユーザー Joe と Ann がいくつかの集中的なタ...
- 質問341 Linux管理者はシステムからUSBドライブを取り外す必要があります...
- 質問342 管理者は、コンソールモードでのみ実行できるスクリプトを使用し
- 質問343 カーネルパラメータを調整するために使用されるコマンドはどれで
- 質問344 新しいセキュリティ ポリシーに準拠するには、管理者は SSH サー...
- 質問345 オーケストレーションに関して「エージェントレス」という用語の
- 質問346 管理者はリモートサーバーにログインするためにRSA SSH鍵ペアを...
- 質問347 Linux システム上の vmlinux ファイルの目的は次のうちどれです...
- 質問348 システムエンジニアは、重要なサーバーを再起動する atjob をス...
- 質問349 アプリケーションコードはGilに保存されています。セキュリティ...
- 質問350 Linux システムが起動に失敗し、次のエラー メッセージが表示さ...
- 質問351 システム管理者は、複数のLinuxシステムへのパッチのインストー...
- 質問352 管理者は Linux サーバーの GUI をリモートで使用したいのですが...
- 質問353 Linux管理者は、開発者がコンテナをデプロイする際にJava 7とJav...
- 質問354 Linux管理者はCompTIA_docというディレクトリを作成中ですが、シ...
- 質問355 ユーザーから、collaborate.company.comにユーザーVLANからアク...
- 質問356 サーバーのアプリケーション ポートがファイアウォールによって
- 質問357 システム管理者は、/etc/nologinファイルが存在する間、root以外...
- 質問358 ある企業では、すべてのサーバーの BIOS を協定世界時で構成し、...
- 質問359 Linux管理者は、Dockerサービスで使用するボリュームをマウント...
- 質問360 多数の異なるサーバーにわたる多数のコンテナをオーケストレーシ
- 質問361 Linux管理者は、ユーザーのホームディレクトリからリモートサー...
- 質問362 Linuxユーザーがシェルを/bin/bashに変更したいと考えています。...
- 質問363 Linux管理者は、アプリケーションソフトウェアをインストールす...
- 質問364 Linux管理者がlogcollectアカウントのパスワードを更新していま...
- 質問365 Linux管理者は、pingコマンドのセキュリティイベントをログに記...
- 質問366 管理者は、サーバーの再起動後に起動に失敗したアプリケーション
- 質問367 Linux管理者は、ログ出力ファイル群を確認し、「denyed」という...
- 質問368 コンパイルのためにソフトウェアをチェックおよび準備するために
- 質問369 管理者は最近ハッキングされた Linux サーバーを分析しています...
- 質問370 会社のポリシーで、ユーザーは Windows サーバーにサードパーテ...
- 質問371 アナリストは、どのパブリック IP アドレスが A 社によって管理...
- 質問372 システム管理者は複数のLinuxマシンに新しいユーザーアカウント...
- 質問373 監視サーバーの役割の目的は次のどれですか?
- 質問374 システム管理者は、ネットワークインターフェース上にリモートコ
- 質問375 システム管理者がリモート システムへのパスワードなしのログイ
- 質問376 システム管理者は、ネットワークおよびインターネット上の他のデ
- 質問377 経験の浅い Linux 管理者は、過去 4 年間の四半期ごとの売上情報...
- 質問378 すべてのユーザーからSFTPサーバーに接続できないという報告があ...
- 質問379 管理者は、TCP ポートや UDP ポートでリッスンしているサービス...
- 質問380 Linux管理者が、FTPサービスを実行できるもののシステムにログイ...
- 質問381 次のサーバー ロールのうち、ハートビート/ポーリング プロセス...
- 質問382 暗号化されたトンネル SOCKS サービスを提供するサーバーは次の...
- 質問383 Linux管理者が、Ubuntuシステム上のソフトウェアおよびアップデ...
- 質問384 初級 Linux 管理者は、システムの起動時にサービスが起動するこ...
- 質問385 システム管理者は新しいワークステーションに Git をインストー...
- 質問386 Linux システム上での実行を最もよく表しているのは次のうちどれ...
- 質問387 Linuxシステム上のMySQLデータベースに接続しているユーザーから...
- 質問388 システム管理者が会社用の Web サーバーを作成し、エンドユーザ...
- 質問389 システム起動後、X Window SystemのGUIログインインターフェース...
- 質問390 ある企業では、平均して3人に1人のユーザーが自社ウェブサイトに...
- 質問391 DevOpsエンジニアは、Linuxサーバーの4000~5000番ポートへの着...
- 質問392 管理者がmyhost上のSSHサーバーのデフォルトポートを2222に変更...
- 質問393 ミラーサイトに repo10 という新しいパッケージリポジトリがイン...
- 質問394 管理者は、ユーザーJoeがLinuxサーバー上で不正なプロセスを実行...
- 質問395 システム管理者は、ip link コマンドを実行して enp0s3 という名...
- 質問396 次の情報のうち、 BIOS 内に保存されるのはどれですか? (正しい...
- 質問397 Linux サーバーを強化する際に、適切なセキュリティ対策と考えら...
- 質問398 ワークステーションからNFSサーバーに大容量ファイルを転送しよ...
- 質問399 Linux管理者が新しいネットワークアダプタをインストールし、起...
- 質問400 Linux 管理者がファイル /home/user/data. txt から ACL を削除...
- 質問401 Linux 管理者は、システムに接続されている USB デバイスを把握...
- 質問402 ドラッグアンドドロップの質問 システム管理者として、ディスク
- 質問403 管理者は、プライマリウェブサーバー www1 上のウェブサイトファ...
- 質問404 Linux管理者は、systemdを使用して2時間ごとにジョブを実行する...
- 質問405 システムがすでにユーザー名とパスワードの認証を実装している場
- 質問406 システム管理者は、別の Git ブランチで監視ソフトウェアの新し...
- 質問407 システム管理者は、自動ロードされたデバイスモジュールの多くが
- 質問408 Linux管理者は、前提条件が満たされているかどうかを確認する必...
- 質問409 実験で生成されたファイルが10万個以上あるため、ディレクトリを...
- 質問410 Linux管理者は、サーバーのファイアウォール上の特定のポートを...
- 質問411 Linux 管理者が Git リポジトリに新しい構成ファイルを追加して...
- 質問412 管理者は、systemdベースのシステム上のアプリケーションのログ...
- 質問413 ネットワーク管理者がLinuxホストにWebサーバーをインストールし...
- 質問414 ユーザーは次のスクリプト ファイルを作成しました: #!/bin/bash...
- 質問415 Linux管理者がLinuxサーバー上でデータベースサービスを起動しよ...
- 質問416 Linux管理者が、終了状態にあるコンテナを多数発見しました。管...
- 質問417 顧客から、Linux本番サーバーのパフォーマンスが不定期に低下し...
- 質問418 システム管理者は、サーバーのパフォーマンス低下を調査していま
- 質問419 Linux 管理者には、情報を一元管理し、検索可能でレポート作成に...
- 質問420 LVMミラーボリュームの片方のレッグが、基盤となる物理ボリュー...
- 質問421 ボリューム上にファイルを作成しているときに、Linux 管理者は次...
- 質問422 Linuxシステムの会計グループのメンバーであるジョーは、会計共...
- 質問423 管理者は、作業用開発ディレクトリをステージング サーバーに安
- 質問424 管理者は、httpd ウェブサーバーでホストされているウェブサイト...
- 質問425 管理者はhosts.csvというCSVファイルを所有しています。hosts.cs...
- 質問426 管理者は、PID 2274 のプロセスのシステム優先度を上げる必要が...
- 質問427 Linux管理者は、コンテナ内にApacheウェブサーバーをデプロイす...
- 質問428 クラウド エンジニアは、IP アドレス 192.168.10.50 からの Linu...
- 質問429 LinuxエンジニアがZIPファイルをダウンロードする必要があり、こ...
