- ホーム
- Microsoft
- MD-102-JPN - Endpoint Administrator (MD-102日本語版)
- Microsoft.MD-102-JPN.v2026-10-30.q163
- 質問74
有効的なMD-102-JPN問題集はJPNTest.com提供され、MD-102-JPN試験に合格することに役に立ちます!JPNTest.comは今最新MD-102-JPN試験問題集を提供します。JPNTest.com MD-102-JPN試験問題集はもう更新されました。ここでMD-102-JPN問題集のテストエンジンを手に入れます。
MD-102-JPN問題集最新版のアクセス
「446問、30% ディスカウント、特別な割引コード:JPNshiken」
Microsoft Intune を含む Microsoft 365 サブスクリプションをお持ちです。
次の要件を満たす Microsoft Defender for Endpoint ソリューションを実装する必要があります。
* 条件付きアクセスを使用して Defender for Endpoint のコンプライアンスを強制します
* デバイス上で疑わしいスクリプトが実行されないようにします
何を構成する必要がありますか? 答えるには、適切な機能を正しい要件にドラッグします。各機能は、1 回、複数回、またはまったく使用されない場合があります。コンテンツを表示するには、ペイン間の分割バーをドラッグするか、スクロールする必要がある場合があります。
注意: 正しい選択ごとに 1 ポイントが付与されます。

次の要件を満たす Microsoft Defender for Endpoint ソリューションを実装する必要があります。
* 条件付きアクセスを使用して Defender for Endpoint のコンプライアンスを強制します
* デバイス上で疑わしいスクリプトが実行されないようにします
何を構成する必要がありますか? 答えるには、適切な機能を正しい要件にドラッグします。各機能は、1 回、複数回、またはまったく使用されない場合があります。コンテンツを表示するには、ペイン間の分割バーをドラッグするか、スクロールする必要がある場合があります。
注意: 正しい選択ごとに 1 ポイントが付与されます。
正解:
Explanation:
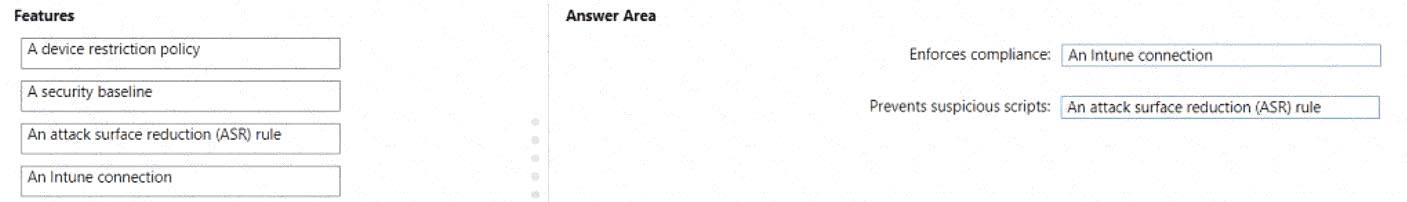
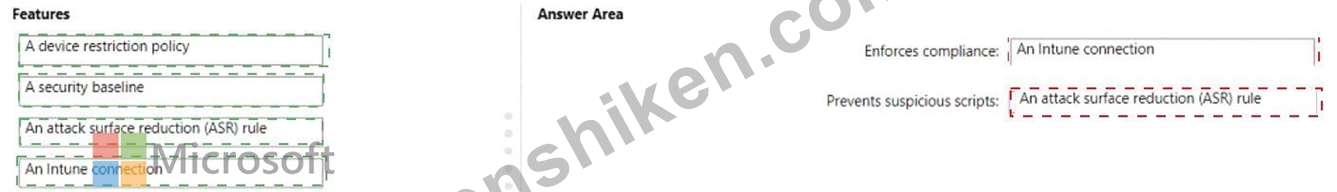
To enforce compliance for Defender for Endpoint by using Conditional Access, you need to configure an Intune connection in the Defender for Endpoint portal. This allows you to use Intune device compliance policies to evaluate the health and compliance status of devices that are enrolled in Defender for Endpoint.
You can then use Conditional Access policies to block or allow access to cloud apps based on the device compliance status. References: https://docs.microsoft.com/en-us/windows/security/threat-protection/microsoft- defender-atp/conditional-access To prevent suspicious scripts from running on devices, you need to configure an attack surface reduction (ASR) rule in Intune. ASR rules are part of the endpoint protection settings that you can apply to devices by using device configuration profiles. You can use the ASR rule "Block Office applications from creating child processes" to prevent Office applications from launching child processes such as scripts or executables.
References: https://docs.microsoft.com/en-us/mem/intune/protect/endpoint-protection-windows-10#attack- surface-reduction-asr-rules

- 質問一覧「163問」
- 質問1 Windows 10 を実行しているコンピューターに機能更新プログラム...
- 質問2 Windows 11 を実行する Computer! という名前のコンピューターが...
- 質問3 Microsoft 365 サブスクリプションがあり、その中に User1 とい...
- 質問4 Microsoft Intune を含む Microsoft 365 サブスクリプションをお...
- 質問5 Windows 10 を実行し、Azure Log Analytics ワークスペースに接...
- 質問6 会社には、複数の Windows 10 デバイスを含む contoso.com とい...
- 質問7 注: この質問は、同じシナリオを提示する一連の質問の一部です。...
- 質問8 Microsoft Intuneを使用するMicrosoft 365サブスクリプションを...
- 質問9 Microsoft Intune Suite を使用する Microsoft 365 サブスクリプ...
- 質問10 オンプレミスのエンタープライズ証明機関 (CA) への PFX 証明書...
- 質問11 Microsoft Deployment Toolkit (MDT) と Windows 展開サービス (...
- 質問12 Microsoft 365 サブスクリプションをお持ちです。 次の表に示す...
- 質問13 次の表に示すユーザーを含む Azure Active Directory Premium プ...
- 質問14 会社では Microsoft Intune を使用してデバイスを管理しています...
- 質問15 Group1 という名前のグループを含む Microsoft 365 E5 サブスク...
- 質問16 Microsoft 365 サブスクリプションをお持ちです。 デバイスを管...
- 質問17 次の表に示すように、3 つのサイトに Microsoft Deployment Tool...
- 質問18 Microsoft Intune が含まれる Microsoft 365 ES サブスクリプシ...
- 質問19 接続1と接続2の計画された変更を実装します ユーザーがデバイス ...
- 質問20 150 台のハイブリッド Azure AD 参加済み Windows デバイスを含...
- 質問21 Windows 10 を実行し、Windows AutoPilot を使用して構成されて...
- 質問22 - DS1 という名前の Microsoft Deployment Toolkit (MDT) 展開共...
- 質問23 あなたはMicrosoft 365のサブスクリプションをお持ちです。Micro...
- 質問24 Azure AD テナントに同期するオンプレミスの Active Directory ...
- 質問25 あなたはMicrosoft 365のサブスクリプションを所有しており、Mic...
- 質問26 Microsoft Intune を使用する Microsoft 365 ES サブスクリプシ...
- 質問27 次の表に示すように、会社には Microsoft Intune に登録されたデ...
- 質問28 Microsoft 365 サブスクリプションがあり、Microsoft Intune を...
- 質問29 Microsoft 365 ES サブスクリプションをお持ちです。 すべてのデ...
- 質問30 ネットワークには Active Directory ドメインが含まれています。...
- 質問31 次の表に示すように、Microsoft Intuneに登録されているWindows ...
- 質問32 次の表に示すように、動的デバイス メンバーシップ タイプを使用...
- 質問33 DS1 という名前の Microsoft Deployment Toolkit (MDT) 展開共有...
- 質問34 ネットワークには、adatum.com という名前の Active Directory ...
- 質問35 Azure Log Analytics ワークスペースを含む Microsoft Azure サ...
- 質問36 50 台の Windows 10 デバイスを含む Azure AD のハイブリッド展...
- 質問37 LEG 部門のコンピューターの技術要件を満たす必要があります。 ...
- 質問38 Windows 11 を実行し、パブリック ネットワークに接続する Clien...
- 質問39 Contoso.com という名前の Azure AD テナントがあり、このテナン...
- 質問40 Microsoft 365 E5 サブスクリプションと 100 台の管理されていな...
- 質問41 次の表に示すユーザーを含む Azure Active Directory (Azure AD)...
- 質問42 Microsoft Intune と Intune データ ウェアハウスを使用します。...
- 質問43 Microsoft 365 E5 サブスクリプションをお持ちです。 名前に「Ma...
- 質問44 どのユーザーが Device6 を Intune に登録できますか?...
- 質問45 Microsoft Intune Suite を使用する Microsoft 365 サブスクリプ...
- 質問46 次の表に示すように、Microsoft Intune に登録されているデバイ...
- 質問47 ネットワークにはオンプレミスの Active Directory ドメインが含...
- 質問48 Microsoft 365 サブスクリプションがあり、その中に User1 とい...
- 質問49 Windows 10 を実行するコンピューターが 100 台あります。サーバ...
- 質問50 Microsoft Intuneに登録されたデバイスを含むMicrosoft 365 E5サ...
- 質問51 Microsoft 36S サブスクリプションがあり、Microsoft Intune を...
- 質問52 ネットワークには Active Directory ドメインが含まれています。...
- 質問53 あなたは、Microsoft Intune を含む Microsoft 365 E5 サブスク...
- 質問54 User1 と User2 が Intune に登録できるデバイスの最大数はいく...
- 質問55 次の表に示すデバイスを含む Microsoft 365 サブスクリプション...
- 質問56 次の表に示すデバイスを含む Microsoft 365 サブスクリプション...
- 質問57 Microsoft 365 E5 サブスクリプションと、Windows 10 を実行する...
- 質問58 1,000 台の iOS デバイスを含む Microsoft 365 サブスクリプショ...
- 質問59 500 台の Android Enterprise デバイスを含む Microsoft 365 サ...
- 質問60 ネットワークには、Azure AD テナントと同期するオンプレミスの ...
- 質問61 Microsoft Intune Suite を使用する Microsoft 365 サブスクリプ...
- 質問62 ハイブリッド Azure AD テナントがあります。 次の図に示すよう...
- 質問63 次の表に示すデバイスを含む Microsoft 365 E5 サブスクリプショ...
- 質問64 Microsoft Intune に登録されている 500 台の macOS デバイスを...
- 質問65 - 次の表に示すデバイスを含む Microsoft 365 サブスクリプショ...
- 質問66 Share 1 という名前の Microsoft Deployment Toolkit (MDT) 展開...
- 質問67 ネットワークには、contoso.com という名前の Active Directory ...
- 質問68 次の表に示すデバイスを含む Azure AD テナントがあります。 (Ex...
- 質問69 Microsoft Intune に登録されている Windows 10 デバイスが 100 ...
- 質問70 contoso.com という名前の Microsoft Entra テナントがあり、こ...
- 質問71 Microsoft 365 サブスクリプションをお持ちです。 すべてのコン...
- 質問72 あなたはMicrosoft 365 E5サブスクリプションを所有しています。...
- 質問73 Microsoft Deployment Toolkit (MDT) がインストールされていま...
- 質問74 Microsoft Intune を含む Microsoft 365 サブスクリプションをお...
- 質問75 お客様は、Microsoft Intuneを使用するMicrosoft 365サブスクリ...
- 質問76 Group1 という名前の Azure AD グループがあります。Group1 には...
- 質問77 注: このセクションには、同じシナリオと問題を扱う1つ以上の質...
- 質問78 お客様は、デバイス1という名前のデバイスを含むMicrosoft 365 E...
- 質問79 Windows 10 を実行し、Microsoft Intune を使用して管理されてい...
- 質問80 Microsoft 365 E5 サブスクリプションをお持ちです。 Microsoft ...
- 質問81 会社所有の Windows デバイス 100 台を交換します。 デバイスを...
- 質問82 Microsoft Intune に登録された Windows 11 デバイスを含む Micr...
- 質問83 Microsoft 365 サブスクリプションをお持ちです。 Windows 10 を...
- 質問84 Microsoft 365 E5 サブスクリプションと、Windows 11 を実行する...
- 質問85 contoso.com という名前の Azure AD テナントがあります。 Windo...
- 質問86 Microsoft Intune Suite を使用する Microsoft 365 サブスクリプ...
- 質問87 Microsoft Intune と Intune データ ウェアハウスを使用します。...
- 質問88 Windows 10 Pro を実行するコンピューターが 25 台あります。 Mi...
- 質問89 オンプレミス ネットワークには、Active Directory ドメイン サ...
- 質問90 あなたは、Device 1、Device2 という名前の 3 台の Windows デバ...
- 質問91 次のデバイス コンプライアンス ポリシー設定を持つ Microsoft I...
- 質問92 Microsoft 365 E5 サブスクリプションがあり、Microsoft Intune ...
- 質問93 Microsoft 365 サブスクリプションをお持ちです。 ユーザーは、M...
- 質問94 Microsoft Intuneに登録されている、Device!という名前のAndroid...
- 質問95 あなたは、Group! という名前のグループと、Android または iOS ...
- 質問96 Microsoft 365 サブスクリプションをお持ちです。 セキュリティ...
- 質問97 次の表に示すデバイスを含む Azure AD テナントがあります。 (Ex...
- 質問98 会社では Microsoft Defender for Endpoint を使用しています。M...
- 質問99 Microsoft Intune Suite を使用する Microsoft 365 サブスクリプ...
- 質問100 Microsoft Intune Suite を使用する Microsoft 365 サブスクリプ...
- 質問101 Microsoft 365 サブスクリプションをお持ちです。 すべてのユー...
- 質問102 Microsoft 365 E5 サブスクリプションがあります。サブスクリプ...
- 質問103 Microsoft Intune を使用し、100 台の Windows 10 デバイスを含...
- 質問104 次の表に示す Windows 10 デバイスがあります。 (Exhibit) デバ...
- 質問105 App1 を購入して割り当てることができるのはどのユーザーですか?...
- 質問106 contoso.com という名前の Azure AD テナントがあります。 Windo...
- 質問107 お客様のネットワークには、contoso.com という名前のオンプレミ...
- 質問108 Microsoft 365 サブスクリプションをお持ちです。 Microsoft Int...
- 質問109 Microsoft Intune Suite を使用する Microsoft 365 サブスクリプ...
- 質問110 ネットワークには Active Directory ドメイン サービス (AD DS) ...
- 質問111 Active Directory に参加し、Microsoft Intune に登録されている...
- 質問112 Microsoft Intune を使用し、次の表に示すユーザーを含む Micros...
- 質問113 User! という名前のユーザーと Appl という名前の Web アプリを...
- 質問114 contoso.com という名前の Azure AD テナントがあります。 ユー...
- 質問115 Windows 11 展開タスクの管理に使用される Microsoft Deployment...
- 質問116 お客様のMicrosoft Entraテナントには、Device1という名前のデバ...
- 質問117 Microsoft Intune を使用し、次の表に示すデバイスを含む Micros...
- 質問118 お客様のネットワークには、contoso.com という名前のオンプレミ...
- 質問119 Windows Autopilot 展開サービスを使用して登録されるデバイスは...
- 質問120 お客様は、Microsoft Intuneを使用するMicrosoft 365サブスクリ...
- 質問121 次の表に示すデバイスを含む Microsoft Entra テナントがありま...
- 質問122 次の表に示すオブジェクトを含む Microsoft 365 テナントがあり...
- 質問123 計画された変更に基づいて Boundary1 を実装します。 192.168.1....
- 質問124 Windows AutoPilot の OOBE 要件を満たす必要があります。 Azure...
- 質問125 次の表に示すリソースを含む Microsoft Intune 展開があります。...
- 質問126 Windows 10 を実行するコンピューターが 200 台あります。コンピ...
- 質問127 Windows 11 Pro を実行するコンピューターがあります。コンピュ...
- 質問128 Microsoft Intune と Microsoft Defender for Endpoint が含まれ...
- 質問129 MKG 部門ユーザーの要件を満たす必要があります。 何をすべきで...
- 質問130 Microsoft 365 テナントと内部証明機関 (CA) があります。 管理...
- 質問131 お客様は、以下の表に示すデバイスを含む Microsoft 365 E5 サブ...
- 質問132 次の表に示すグループを含む Microsoft Entra テナントがありま...
- 質問133 どのデバイスが準拠しているかを評価しています。 次の各文につ
- 質問134 Microsoft Deployment Toolkit (MDT) 展開共有があります。 展開...
- 質問135 Microsoft Intune Suite を使用する Microsoft 365 サブスクリプ...
- 質問136 デバイス管理要件を満たすソリューションを推奨する必要がありま
- 質問137 Microsoft Intune を使用する Microsoft 365 E5 サブスクリプシ...
- 質問138 MDM 展示に表示されている MDM セキュリティ ベースライン プロ...
- 質問139 次の表に示すデバイスを含む Microsoft 365 E5 サブスクリプショ...
- 質問140 Microsoft Intuでデバイス構成プロファイルを作成しています プ...
- 質問141 Group1 と Group2 という 2 つのセキュリティ グループを含む Mi...
- 質問142 Microsoft 365 サブスクリプションがあり、Microsoft Intune Sui...
- 質問143 - Microsoft 365 サブスクリプションがあります。サブスクリプシ...
- 質問144 ネットワークには Active Directory ドメインが含まれています。...
- 質問145 Microsoft Intune Suite を使用する Microsoft 365 サブスクリプ...
- 質問146 お客様はMicrosoft 365 E5サブスクリプションをご利用中です。す...
- 質問147 Microsoft 365 サブスクリプションがあります。サブスクリプショ...
- 質問148 DS1 という名前の Microsoft Deployment Toolkit (MDT) 展開共有...
- 質問149 あなたの会社には次のようなインフラストラクチャがあります。 *...
- 質問150 Microsoft 365 E5 サブスクリプションをお持ちです。すべてのデ...
- 質問151 お客様は、以下の表に示すように、Microsoft Intuneに登録された...
- 質問152 Microsoft Intune Suite を実装しました。 次の表に示すように、...
- 質問153 Microsoft 365 E5 サブスクリプションをお持ちです。 すべての W...
- 質問154 Server1 という名前のサーバーと、Windows 8.1 を実行するコンピ...
- 質問155 Microsoft Intune に登録されているデバイスの種類は次のとおり...
- 質問156 Windows 11 を実行する Computer1 という名前のコンピューターを...
- 質問157 Microsoft Intune を使用して個人用デバイスと企業デバイスを管...
- 質問158 会社には、Windows 10 を実行する Computer1 という名前のコンピ...
- 質問159 次の表に示す仮想マシンを含む Hyper-V ホストがあります。 (Exh...
- 質問160 Microsoft Intune に登録された 1,000 台の Windows 11 デバイス...
- 質問161 Azure AD テナントと、Azure AD に参加し、Microsoft Intune を...
- 質問162 次の表に示すオンプレミス サーバーがあります。 (Exhibit) Andr...
- 質問163 Microsoft Intune を含む Microsoft 365 サブスクリプションがあ...

[×]
Download PDF File
Enter your email address to download Microsoft.MD-102-JPN.v2026-10-30.q163.pdf