次の表に示すユーザーを含むcontoso.comという名前のAzure Active Directory(Azure AD)テナントがあります。
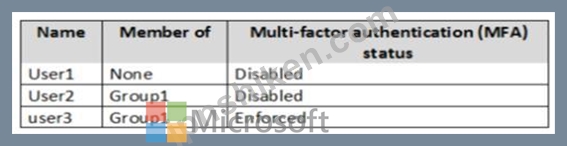
Azure AD Privileged Identity Management (PIM) is enabled for the tenant.
In PIM, the Password Administrator role has the following settings:
* Maximum activation duration (hours): 2
* Send email notifying admins of activation: Disable
* Require incident/request ticket number during activation: Disable
* Require Azure Multi-Factor Authentication for activation: Enable
* Require approval to activate this role: Enable
* Selected approver: Group1
You assign users the Password Administrator role as shown in the following table.
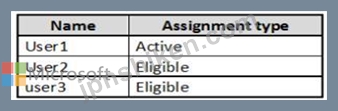
以下の各ステートメントについて、ステートメントが真である場合は「はい」を選択します。それ以外の場合は、「いいえ」を選択します。
注:それぞれの正しい選択には1ポイントの価値があります。
Azure AD Privileged Identity Management (PIM) is enabled for the tenant.
In PIM, the Password Administrator role has the following settings:
* Maximum activation duration (hours): 2
* Send email notifying admins of activation: Disable
* Require incident/request ticket number during activation: Disable
* Require Azure Multi-Factor Authentication for activation: Enable
* Require approval to activate this role: Enable
* Selected approver: Group1
You assign users the Password Administrator role as shown in the following table.
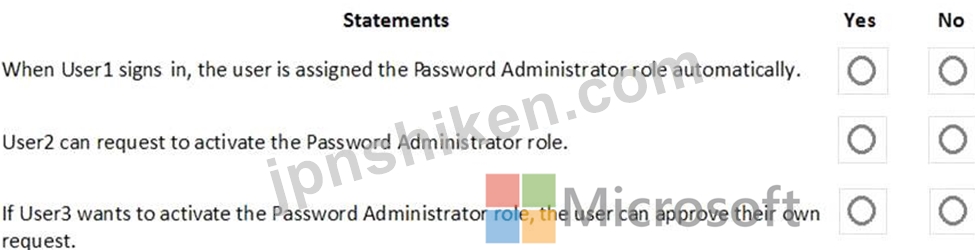
以下の各ステートメントについて、ステートメントが真である場合は「はい」を選択します。それ以外の場合は、「いいえ」を選択します。
注:それぞれの正しい選択には1ポイントの価値があります。


