- ホーム
- CompTIA
- CAS-005-JPN - CompTIA SecurityX Certification Exam (CAS-005日本語版)
- CompTIA.CAS-005-JPN.v2026-11-06.q249
- 質問143
有効的なCAS-005-JPN問題集はJPNTest.com提供され、CAS-005-JPN試験に合格することに役に立ちます!JPNTest.comは今最新CAS-005-JPN試験問題集を提供します。JPNTest.com CAS-005-JPN試験問題集はもう更新されました。ここでCAS-005-JPN問題集のテストエンジンを手に入れます。
CAS-005-JPN問題集最新版のアクセス
「604問、30% ディスカウント、特別な割引コード:JPNshiken」
ウェブサイトの脆弱性スキャンを実行したところ、次の暗号化スイートが見つかりました。
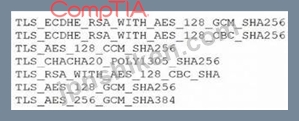
次のアクションのうちどれが脆弱性を修正しますか?
次のアクションのうちどれが脆弱性を修正しますか?
正解:A
Cipher suites that use CBC (Cipher Block Chaining), such as
TLS_ECDHE_RSA_WITH_AES_128_CBC_SHA256 and
TLS_RSA_WITH_AES_128_CBC_SHA, are vulnerable to padding oracle and related attacks.
Removing CBC-based ciphers ensures only modern and secure cipher suites (e.g., GCM, ChaCha20) are used, remediating the vulnerability.
TLS_ECDHE_RSA_WITH_AES_128_CBC_SHA256 and
TLS_RSA_WITH_AES_128_CBC_SHA, are vulnerable to padding oracle and related attacks.
Removing CBC-based ciphers ensures only modern and secure cipher suites (e.g., GCM, ChaCha20) are used, remediating the vulnerability.

- 質問一覧「249問」
- 質問1 SOCエンジニアは、一連のタスクを最小限の労力で迅速に自動化す...
- 質問2 プロセッサが暗号化キーを知らない場合でも、暗号化されたデータ
- 質問3 ジョン・ドウのメールアカウントが侵害されました。攻撃者のジョ
- 質問4 最高セキュリティ責任者(CSO)は、セキュリティチームに対し、以...
- 質問5 ユーザーが http://10.1.1.1 のウェブページにアクセスしようと...
- 質問6 ある企業が顧客向けに外部アプリケーションを作成しました。セキ
- 質問7 グローバル企業のセキュリティ管理者が、個人識別情報を含むシス
- 質問8 DNP3にとってセキュリティ上の懸念事項となるのは次のうちどれで...
- 質問9 ある組織は、クラウドプロバイダーが管理する無料の暗号鍵ではな
- 質問10 ある企業が最近マルウェアに感染しました。根本原因分析の結果、
- 質問11 ある企業がWindows ServerからLinuxベースのサーバーに移行しよ...
- 質問12 セキュリティアナリストは、セキュリティインシデントに関連する
- 質問13 ある組織は、特定の脆弱性の影響を受ける資産をより正確に特定す
- 質問14 敵対的シミュレーション演習中に、外部チームが組織に検知される
- 質問15 あるウェブサービスプロバイダーが、現在実施されていない要件を
- 質問16 セキュリティチームは、通常の営業時間外に、あり得ない移動やブ
- 質問17 最近のセキュリティ イベント中に、非本番環境から本番環境への
- 質問18 企業の内部ネットワークでセキュリティ侵害が発生しており、脅威
- 質問19 セキュリティ管理者はアラートを自動化する必要があります。サー
- 質問20 アプリケーションセキュリティエンジニアがワークロードのIAM構...
- 質問21 最高情報セキュリティ責任者(CISO)がセキュリティチームに対し、...
- 質問22 ある企業が、セキュリティ上の脆弱性を特定し、関係者を潜在的な
- 質問23 インシデント対応チームは、複数のワークステーションのオフライ
- 質問24 ある企業は、開発環境で個人情報(PII)データに関するインシデ...
- 質問25 IT部門は現在、エンタープライズDLPソリューションの導入に取り...
- 質問26 あるアプリケーションでは、個人情報(PII)の保存が必要です。シ...
- 質問27 最近合併した2社は、社内認証ストアを統合することなく、両社間
- 質問28 セキュリティアナリストが、一般公開されている銀行アプリケーシ
- 質問29 外部のSaaSソリューションユーザーから、ロールベースアクセス制...
- 質問30 ある政府機関は、国際ローミング中に政府発行のデバイスで携帯電
- 質問31 ある下請け業者が、大手航空機メーカー向けにセーフティクリティ
- 質問32 モバイル管理者は、管理対象デバイスに適切なモバイル設定が適用
- 質問33 メールセキュリティソリューションのレビュー中に、セキュリティ
- 質問34 サイトAのSCADAコントローラに障害が発生した場合、エンジニアは...
- 質問35 セキュリティ担当者は、企業環境にサードパーティ製ソリューショ
- 質問36 ある企業は、APIリクエストに基づく新しいサーバーレスソリュー...
- 質問37 限られた予算で運営する場合に組織のリスク許容度を決定すること
- 質問38 同社の顧客サービスチームは、新たな脆弱性に関する顧客からの問
- 質問39 セキュリティアナリストは、業界のベストプラクティスと確立され
- 質問40 セキュリティアーキテクトがコードの一部を調査した結果、以下の
- 質問41 組織は特殊なエンドポイントを管理したいと考えており、次のよう
- 質問42 ある企業は、顧客契約において、アプリケーションの脆弱性を特定
- 質問43 A社とD社は合併します。A社のコンプライアンスレポートによると...
- 質問44 ある組織が新しいソフトウェアの導入を計画しています。プロジェ
- 質問45 アナリストは、企業への攻撃を成功させるための複数の解決策を用
- 質問46 リアルタイムの財務処理を行う組織が、新しいバックアップソリュ
- 質問47 ソフトウェアエンジニアは、Webアプリケーションの開発をサポー...
- 質問48 セキュリティアーキテクトは、以下のようなデータフィールドへの
- 質問49 ある企業は、業界標準に準拠するために、クラウド環境のコンプラ
- 質問50 過去に傍受された通信は、現在の暗号鍵が将来侵害された場合でも
- 質問51 ベンダーロックインに伴うリスクとして、次のうちどれが該当しま
- 質問52 セキュリティ アナリストは、特定のユーザーが会社のリソースに
- 質問53 SOCアナリストは、侵入テスト担当者がペイロードの作成と実行に...
- 質問54 最高情報セキュリティ責任者は、組織のベースラインワークロード
- 質問55 セキュリティアーキテクトは、標的型攻撃と思われる攻撃によって
- 質問56 セキュリティ担当者は、夜間にMFAプッシュ通知が過剰に届くとい...
- 質問57 以下のAIに関する懸念事項のうち、入力データのサニタイズによっ...
- 質問58 監査結果によると、いくつかのユーザーエンドポイントはフルディ
- 質問59 セキュリティエンジニアは、組織のバグ報奨金プログラムを通じて
- 質問60 セキュリティアーキテクトが、検出機能をサポートするために、組
- 質問61 規制対象企業がインフラ全体の刷新を進めている。同社は、業務上
- 質問62 保護対象の企業データが最近流出しました。SOCはネットワーク侵...
- 質問63 ある企業は、脆弱性を迅速に修正し、本番環境へデプロイするため
- 質問64 セキュリティ エンジニアが ECC を格子ベースの暗号化技術に置き...
- 質問65 あるソフトウェア開発者が、新しいソフトウェアパッケージに必要
- 質問66 病院が空調システムを遠隔で第三者に監視させる場合の要件は以下
- 質問67 ある企業は、社内で開発されたビジネスクリティカルなアプリケー
- 質問68 あるグローバル製造企業は、製品製造に不可欠な社内アプリケーシ
- 質問69 セキュリティエンジニアが、サーバークラッシュ後にSIEMログを確...
- 質問70 セキュリティチームは、特定の社内リソースにアクセスできないユ
- 質問71 ある組織は、従業員がテンプレート開発、編集、調査、スケジュー
- 質問72 最近のコンプライアンス監査で明らかになった重要な調査結果によ
- 質問73 セキュリティエンジニアが、ドメイン間のデータと通信をセグメン
- 質問74 ある組織は、新たなソーシャルエンジニアリング攻撃やフィッシン
- 質問75 ある企業のヘルプデスクには、財務部門からwww.bank.comへのアク...
- 質問76 ある企業は最近、新しいアプリケーションをサポートするために、
- 質問77 サイバーセキュリティアーキテクトは、脆弱性管理を改善し、多数
- 質問78 ある組織は、すべてのインスタンスにわたって安全なクラウドアー
- 質問79 ソフトウェア開発ライフサイクルにおけるセキュリティ監査の一環
- 質問80 アーキテクトは、外部サービスをサポートするために外部インフラ
- 質問81 サイバーセキュリティアーキテクトは、最近複数の企業を買収した
- 質問82 コンテナを使用してアプリケーションを実行する企業は、プライベ
- 質問83 量子コンピューティングの進歩により、企業や国が新しい暗号化ア
- 質問84 ある企業は、自社のVPNソリューションにゼロデイ脆弱性を発見し...
- 質問85 セキュリティエンジニアは、次の要件を満たすソリューションを開
- 質問86 データ漏洩を防ぐために、企業のセキュリティ リーダーはユーザ
- 質問87 ある企業は、研究成果を業務に役立てることを目指し、研究能力へ
- 質問88 最高情報セキュリティ責任者(CIO)は、ランサムウェアによる業...
- 質問89 コンプライアンス担当者が事業影響分析を実施しており、事業部門
- 質問90 ある企業のSIEM(セキュリティ情報イベント管理システム)は、誤検...
- 質問91 法廷でデジタル証拠を提出するには、その証拠は以下の条件を満た
- 質問92 シミュレーション 製品開発チームは、リリース前にレビューを受
- 質問93 セキュリティアナリストがJavaで書かれた新しいアプリケーション...
- 質問94 セキュリティ エンジニアには次の要件が与えられます。 * エンド...
- 質問95 意思決定の参考となる大量の行動観察データを収集するプロセスを
- 質問96 システム管理者は、継続的なスキャン活動の結果として生じた脆弱
- 質問97 第三者機関が、顧客の生データを見ることなく、顧客のデータを分
- 質問98 インシデント対応訓練後、セキュリティ管理者は以下の表を確認し
- 質問99 クラウドエンジニアは、以下の点について適切な解決策を特定する
- 質問100 最近の評価において、セキュリティアナリストは以下の点を観察し
- 質問101 セキュリティエンジニアは、特定のリスクを軽減するためのMDMソ...
- 質問102 あるゲーム開発者は新規市場への参入を目指しており、法律顧問か
- 質問103 セキュリティアーキテクトは、SOCチーム向けに以下の要件を満た...
- 質問104 ある組織は、以下のデータ型を含むデータ分類ポリシーに基づいて
- 質問105 シミュレーション ある組織は、災害復旧と事業継続のための計画
- 質問106 インシデントが発生した後、チームは教訓のレビュー中に次のよう
- 質問107 ある組織は、自社のインフラストラクチャにおける脆弱性を特定す
- 質問108 アナリストは、脅威ハンティング機能を実行する際に、侵入分析の
- 質問109 管理者は、社内のモバイルデバイス群をPKIに統合し、デバイスのW...
- 質問110 監査の結果、旧型プラットフォームが30日以上ログを保持していな...
- 質問111 最近、同じ業種の2つの大手エンジニアリング企業が、サイバー脅
- 質問112 セキュリティアナリストが、ユーザーが特定の数字の順序で0から9...
- 質問113 企業の事業影響度分析(BIA)では、1時間以上のデータ損失は事業に...
- 質問114 セキュリティ管理者は、Web サイトのコンポーネントから次のコー...
- 質問115 AIモデルに対するサービス拒否攻撃を最もよく説明しているのは、...
- 質問116 セキュリティエンジニアが、マルチホーム構成のLinuxシステムに...
- 質問117 ある企業は、ビジネスアナリストが購入依頼のリンクを含むメール
- 質問118 外部の脅威アクターが公共インフラプロバイダーを攻撃した。この
- 質問119 ある企業は脆弱性管理プログラムに問題を抱えています。新しいデ
- 質問120 営業時間外に、リモートコンソールアプリケーションから建物内の
- 質問121 シミュレーション あなたは、会社の特権ネットワークから得られ
- 質問122 セキュリティエンジニアは、OpenSSHベースのアプリケーションに...
- 質問123 ある製薬会社は、化学物質の製造に自動制御システムを採用してい
- 質問124 ある組織は、タイポスクワッティングを利用したフィッシングキャ
- 質問125 企業のアプリケーションのセキュリティ監査で、顧客アカウントの
- 質問126 セキュリティアナリストが次のログを確認しています: (Exhibit) ...
- 質問127 セキュリティイベントの調査中、アナリストはユーザーが不明な送
- 質問128 セキュリティアナリストは、サポート対象外のオペレーティングシ
- 質問129 最近の監査で、次の情報に基づいて、ある会社のシステムが評価さ
- 質問130 脆弱性評価中にスキャンを行うと、次の結果が明らかになります。
- 質問131 セキュリティアナリストが次の脆弱性評価レポートを確認していま
- 質問132 ある企業が、顧客向けにビデオトレーニングを提供する新しいオン
- 質問133 ある企業が、重要なワークロードをデータセンターからクラウドに
- 質問134 ソフトウェア開発会社は、ソフトウェアサプライチェーンにおける
- 質問135 セキュリティ アナリストが次の認証ログを確認しています。 (Exh...
- 質問136 ある脅威インテリジェンス企業の事業目標は、顧客がAPIを介して...
- 質問137 ある企業は、グローバル企業ネットワーク全体に展開されているソ
- 質問138 AIの出力が不正確になる理由を最もよく説明しているのは、次のう...
- 質問139 監査担当者が、インシデントの原因を特定するために、Webアプリ...
- 質問140 開発者は、ミッションクリティカルなアプリケーションを保護する
- 質問141 ある企業が、データベースに保存されているデータを隠蔽するため
- 質問142 システムエンジニアは、リモートワークのみの従業員向けにSaaSア...
- 質問143 ウェブサイトの脆弱性スキャンを実行したところ、次の暗号化スイ
- 質問144 ある組織は、ランサムウェア攻撃への備えが不十分であると判断し
- 質問145 あるホテルチェーンは、顧客が従業員の介助なしに客室のチェック
- 質問146 ベンダー評価の際、アナリストは監査レポートに含まれる補完的な
- 質問147 最近、ユーザー認証に関するセキュリティインシデントがいくつか
- 質問148 クラウドエンジニアは、メールの認証をサポートし、メールセキュ
- 質問149 同業他社を標的としたマルウェア攻撃の報告を受け、ある組織は、
- 質問150 ギャップ分析の結果、ある組織はBYOD(私物端末の業務利用)が重大...
- 質問151 ある組織の取締役会は、最高情報セキュリティ責任者に対し、第三
- 質問152 インフラ最適化計画の一環として、ある企業は統合アーキテクチャ
- 質問153 セキュリティ アナリストが SIEM を確認して、次のレポートを生...
- 質問154 セキュリティアナリストは、以前の通信なしでフィッシング攻撃を
- 質問155 病院の警備チームは、患者が画面に表示されているものを見ないよ
- 質問156 エンジニアがレガシーコードを最新のアプリケーションに手動で統
- 質問157 最新およびレガシーの金融アプリケーションを混在させたサービス
- 質問158 ITチームは、アカウントがロックアウトされているという従業員か...
- 質問159 ある企業は、ソフトウェア開発ライフサイクルにおけるセキュアコ
- 質問160 システム管理者は、社内のAIベースのツールを使用して、APIを使...
- 質問161 組織は、外部の要件に従ってシステムとデータを分類する必要があ
- 質問162 ある組織が、その組織が使用するウェブサーバーアプリケーション
- 質問163 現在、ある企業は勤務時間外に発生するインシデントへの対応を、
- 質問164 コンプライアンスマネージャーは、環境におけるリスクを特定する
- 質問165 ある企業が、インバウンド接続に関連する不審なアクティビティを
- 質問166 ある企業が、自社のウェブサイトに関して顧客から複数の苦情を受
- 質問167 侵入テスト担当者が、Webアプリケーションで予期しない動作を引...
- 質問168 グローバルメーカーの主席セキュリティアナリストが、ICSネット...
- 質問169 ある企業が最近、製造工場を買収しました。買収企業は、セキュリ
- 質問170 セキュリティアナリストは、静的アプリケーションのセキュリティ
- 質問171 セキュリティアーキテクトは、DevSecOpsおよびSOARイニシアチブ...
- 質問172 セキュリティ担当者は、特別プロジェクトに従事する全職員に対し
- 質問173 ユーザーがヘルプデスクにチケットを送信し、アカウントが時々認
- 質問174 図に示すネットワークにおいて、ネットワークセキュリティアーキ
- 質問175 ある企業が、セキュリティ責任者(CISO)が関連する法令遵守規則を...
- 質問176 DevOps エンジニアが、Kubernetes の本番環境にアプリケーション...
- 質問177 サイバーセキュリティインシデント発生後、セキュリティアナリス
- 質問178 最近のセキュリティ監査に基づき、ある企業は、境界防御戦略が近
- 質問179 セキュリティアナリストが不審なログインアクティビティを調査し
- 質問180 ある企業が、Webアプリケーションの新しいバージョンを本番環境...
- 質問181 他の暗号化方式と比較した場合、準同型暗号化の利点を最もよく表
- 質問182 ある企業では、他のシステムと比較してタイムスタンプが変更され
- 質問183 セキュリティエンジニアは、開発者エンドポイントとクラウドプロ
- 質問184 セキュリティアナリストは、最新の脆弱性スキャン中に、会社の専
- 質問185 ある企業は、自社製品の一部であるサードパーティ製ハードウェア
- 質問186 レガシーアプリケーションに対するSASTレポートの結果に基づき、...
- 質問187 セキュリティエンジニアは、一部の旧式システムが依然として使用
- 質問188 セキュリティ エンジニアは、コンテナー イメージに対して次の要...
- 質問189 キオスク型ワークステーションを提供する企業が、ワークステーシ
- 質問190 金融業界の複数の企業が同様の事件の影響を受けた後、脅威インテ
- 質問191 ある組織は最近、新しいメールDLPソリューションを導入しました...
- 質問192 セキュリティチームは、リターン指向プログラミングを悪用した攻
- 質問193 セキュリティエンジニアが、ニューヨーク市とアトランタ間のサイ
- 質問194 ある企業は、保護されるべき知的財産データを備えた研究施設を実
- 質問195 ある組織は最近、組織環境における情報セキュリティ管理体制の監
- 質問196 複数のユーザーがシステムへのログイン時にMFA(多要素認証)の使...
- 質問197 ある企業が最近、ランサムウェア攻撃に見舞われました。同社はRP...
- 質問198 ある企業が、サブスクリプション型サービスの電子商取引を行うた
- 質問199 ある企業は、OTシステムを社内ネットワークの他の領域から隔離し...
- 質問200 企業のSIEMは、企業の資産インベントリとユーザーイベントを関連...
- 質問201 準同型暗号化の一般的な使用例を最もよく表しているのは次のうち
- 質問202 押収したノートパソコンからファイルハッシュを取得する最も適切
- 質問203 24時間稼働の製造施設の情報セキュリティマネージャーは、組織に...
- 質問204 リモートワークを推進するグローバル企業が新しいVPNソリューシ...
- 質問205 災害復旧計画を作成する際に、以下の項目のうちどれを含めるべき
- 質問206 アナリストは、導入中の新しいアプリケーションのリスク評価を実
- 質問207 組織全体は、暗号化された資料に個別にアクセスできる従業員によ
- 質問208 小売業界のISACは最近、ソーシャルエンジニアリングの手口に関す...
- 質問209 最近の報告によると、ソフトウェアツールが悪用されているようで
- 質問210 ある組織の脆弱性管理チームは、本番サーバーのスキャン結果から
- 質問211 セキュリティエンジニアが、社内で開発されたWebアプリケーショ...
- 質問212 ある組織は、脅威モデリング機能を含むSOCの構築を目的としたセ...
- 質問213 最新のリスク評価を受けて、最高情報セキュリティ責任者(CISO)は...
- 質問214 開発者は、本番環境での使用を想定して、個人用ラップトップで暗
- 質問215 セキュリティエンジニアは、本番環境に導入される前に、本番コン
- 質問216 脆弱性評価中にスキャンを行うと、次の結果が明らかになります。
- 質問217 ある企業は、クラウドベースのサービスを更新するために、インフ
- 質問218 ある組織は、マルチプラットフォーム環境全体にわたるインシデン
- 質問219 ある大規模組織が、世界中のユーザーが利用できる生成AIプラット...
- 質問220 セキュリティアーキテクトは、エンタープライズシステムの耐障害
- 質問221 データ流出の申し立てを調査している地方自治体は、悪意のあるユ
- 質問222 セキュリティエンジニアは、会社のノートパソコンが盗難に遭った
- 質問223 ユーザーがアプリケーションへのアクセスに関する問題をヘルプデ
- 質問224 最近発生したセキュリティインシデントを調査した後、SOCアナリ...
- 質問225 COL システムに依存している企業は、新しいソリューションが利用...
- 質問226 長期間にわたり、少数のネットワーク侵入試行が継続的に発生して
- 質問227 ある組織が最近、異なるEDRソリューションを運用している別の企...
- 質問228 ある組織では最近、購入凍結を実施し、エンドポイントのライフサ
- 質問229 侵入テスト担当者は、以下のルーター設定を検証します。 set-sys...
- 質問230 セキュリティアナリストは、正当なサードパーティボット関連トラ
- 質問231 攻撃者はハードウェアメーカーのコードベースに侵入し、コードが
- 質問232 ウェブアプリケーションサーバーが、パッチ未適用のリモートコー
- 質問233 セキュリティエンジニアがレガシーサーバーを評価しており、FTP...
- 質問234 シミュレーション IPSecソリューションが導入されています。VPN...
- 質問235 ある企業は、安全性の低いネットワーク上で文書を転送するための
- 質問236 マルウェア研究者は、認証情報窃取マルウェアが特定のメモリレジ
- 質問237 セキュリティアーキテクトは、社内開発アプリケーションのソフト
- 質問238 エンジニアがオンプレミスでホストされているWebアプリケーショ...
- 質問239 従業員はバッジを使って勤務時間を記録します。バッジリーダーは
- 質問240 SIEM(セキュリティ情報イベント管理)システムは、最近リポジトリ...
- 質問241 ある中央銀行は、ハードウェアのサプライチェーンにおいて、特定
- 質問242 ある企業が最近SaaS企業を買収し、ギャップ分析を実施しました。...
- 質問243 境界ファイアウォール構成を検証するためのベスト プラクティス
- 質問244 最近、ある医療システムがランサムウェア攻撃に見舞われました。
- 質問245 セキュリティアナリストが、公開リポジトリにある以下のコードに
- 質問246 侵入テスト中に、複数のユーザーからネットワーク上の特定のファ
- 質問247 ソフトウェア会社は、社内のコード リポジトリに基づいて新しい
- 質問248 システム管理者は、企業のクラウドストレージ環境におけるセキュ
- 質問249 内部ユーザーは、外部組織の受信者を除くすべての受信者に暗号化
