- ホーム
- CompTIA
- CAS-005-JPN - CompTIA SecurityX Certification Exam (CAS-005日本語版)
- CompTIA.CAS-005-JPN.v2026-09-09.q222
- 質問8
有効的なCAS-005-JPN問題集はJPNTest.com提供され、CAS-005-JPN試験に合格することに役に立ちます!JPNTest.comは今最新CAS-005-JPN試験問題集を提供します。JPNTest.com CAS-005-JPN試験問題集はもう更新されました。ここでCAS-005-JPN問題集のテストエンジンを手に入れます。
CAS-005-JPN問題集最新版のアクセス
「604問、30% ディスカウント、特別な割引コード:JPNshiken」
管理者は次のログを確認し、サイト間トンネル障害の根本原因を特定します。
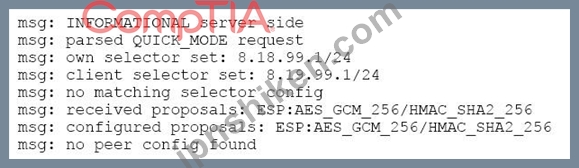
障害を最も効果的に修正するために管理者が実行する必要があるアクションは次のうちどれですか?
障害を最も効果的に修正するために管理者が実行する必要があるアクションは次のうちどれですか?
正解:C
The IKE log is explicitly failing at Quick Mode with "no matching selector config," even though the crypto proposals line up perfectly. That means the tunnel's traffic-selector (the local/remote subnets) doesn't match the policy on one side. In this case the peer is offering 8.19.99.1/24 (and expecting 8.18.99.1/24 on our side), but our IPSec policy likely only permits, for example,
8.19.99.0/24 ↔ 8.18.99.0/24. By adding the actual /24 network (e.g. 8.19.99.0/24) or the specific
/24 selector that the peer is initiating as a permitted initiator, the Quick Mode selectors will align and the tunnel will establish.
8.19.99.0/24 ↔ 8.18.99.0/24. By adding the actual /24 network (e.g. 8.19.99.0/24) or the specific
/24 selector that the peer is initiating as a permitted initiator, the Quick Mode selectors will align and the tunnel will establish.

- 質問一覧「222問」
- 質問1 ある企業は、顧客との契約において、アプリケーションの脆弱性を
- 質問2 セキュリティエンジニアがレガシーサーバーを評価しており、FTP...
- 質問3 セキュリティアナリストがJavaで書かれた新しいアプリケーション...
- 質問4 サイバーセキュリティインシデント発生後、セキュリティアナリス
- 質問5 企業のSIEMはログソースに関する情報を収集します。次のようなレ...
- 質問6 シミュレーション 製品開発チームは、リリース前にレビュー用に
- 質問7 IDおよびアクセス管理チームは、継続的な監視のためにSIEMにログ...
- 質問8 管理者は次のログを確認し、サイト間トンネル障害の根本原因を特
- 質問9 シミュレーション ある組織は災害復旧と業務継続を計画しており
- 質問10 セキュリティアナリストは、本番環境のアプリケーションサーバー
- 質問11 セキュリティエンジニアは、次の要件を満たすソリューションを開
- 質問12 組織は特殊なエンドポイントを管理したいと考えており、次のよう
- 質問13 最近、同じ業種の大手エンジニアリング企業2社が、サイバー脅威
- 質問14 セキュリティアナリストは、以前の通信なしでフィッシング攻撃を
- 質問15 ある企業が、インバウンド接続に関連する不審なアクティビティを
- 質問16 プログラマーは、ユーザーが誤った資格情報を提供した場合に認証
- 質問17 セキュリティチームは、Webサーバーのパフォーマンスに問題を引...
- 質問18 セキュリティ エンジニアは、次の要件を満たすソリューションを
- 質問19 ある組織が新しいソフトウェアの導入を計画しています。プロジェ
- 質問20 リモートワークを推進するグローバル企業が新しいVPNソリューシ...
- 質問21 システム管理者は、社内アプリケーションに新しくリリースされた
- 質問22 技術者がログを確認したところ、3ヶ月間にわたって大量のファイ
- 質問23 DASTスキャン中に、Webアプリケーションの構築に使用されたオー...
- 質問24 ISACは、ソーシャルメディアで使用されている画像に関する最新の...
- 質問25 ある企業で最近、高度な攻撃者がドメインコントローラーのハード
- 質問26 ある中央銀行は、ハードウェアのサプライチェーンにおいて、特定
- 質問27 アプリケーションの実行にコンテナを使用している企業は、プライ
- 質問28 ある企業は、インフラストラクチャ コードをリモート リポジトリ...
- 質問29 セキュリティアーキテクトは、買収した海外のソフトウェア会社が
- 質問30 組織は内部システムデータへのアクセスを提供する必要があります
- 質問31 開発チームは、侵害の兆候(IOC)を共有するためのウェブサイト...
- 質問32 ある企業は、実稼働環境に導入されたコンテナを強化するためのポ
- 質問33 新しいソフトウェア開発手法の一環として、プログラムマネージャ
- 質問34 ある組織は、開発者が成果物を本番環境に直接デプロイできないよ
- 質問35 ある組織は、企業のエンドポイントにおけるソフトウェアアプリケ
- 質問36 ソフトウェア開発チームは社内テスト用に有効なデータを必要とし
- 質問37 新しいオンラインファイルホスティングサービスが提供されます。
- 質問38 クラウド セキュリティ アーキテクトには、次の点を考慮して適切...
- 質問39 企業は複数の脆弱性への対策を管理する必要があります。そのため
- 質問40 セキュリティエンジニアは、ドメイン間のデータと通信をセグメン
- 質問41 ある企業が、世界各地から調達したハードウェアとソフトウェアの
- 質問42 ある企業は今年、アプリケーションセキュリティエンジニアごとに
- 質問43 同社の顧客サービスチームは、新たな脆弱性に関する顧客からの問
- 質問44 量子コンピューティングの進歩により、企業や国が新しい暗号化ア
- 質問45 MDM ソフトウェアから取得されるデバイス イベント ログは次のと...
- 質問46 セキュリティアナリストが次のログを確認しています: (Exhibit) ...
- 質問47 攻撃者はハードウェアメーカーのコードベースに侵入し、コードが
- 質問48 リモートワークフォースを持つ組織に、次の要件を持つ新しいクラ
- 質問49 リモートワークモデルに移行する企業では、会社所有のデバイスが
- 質問50 最近の監査で、次の情報に基づいて、ある会社のシステムが評価さ
- 質問51 最近の障害発生後、あるソフトウェアエンジニアリング会社が開発
- 質問52 ある企業が、機密情報や個人を特定できる情報を扱うAIモデルを導...
- 質問53 セキュリティ アナリストは、特定のユーザーが会社のリソースに
- 質問54 セキュリティコンサルタントが、デジタル証拠の保存に関するベス
- 質問55 セキュリティチームは、修復の進捗状況を追跡するためにチケット
- 質問56 ある下請け業者が、大手航空機メーカー向けにセーフティクリティ
- 質問57 セキュリティ担当者は、特別プロジェクトに従事する全職員に対し
- 質問58 ある組織では現在、IDS、ファイアウォール、DLPシステムを導入し...
- 質問59 セキュリティエンジニアは、定期的にリリースされる新しい検出機
- 質問60 セキュリティアナリストは、ワークステーションからのすべてのア
- 質問61 ある企業は、自社のVPNソリューションにゼロデイ脆弱性を発見し...
- 質問62 ソフトウェア会社は、社内のコード リポジトリに基づいて新しい
- 質問63 セキュリティエンジニアは、企業のプライベートクラウド内に複数
- 質問64 セキュリティ アーキテクトは、安全なコーディング プラクティス...
- 質問65 ある企業が顧客向けに外部アプリケーションを開発しました。セキ
- 質問66 A社はB社を買収し、買収が組織全体の攻撃対象領域にどのような影...
- 質問67 ネットワークエンジニアは、常時VPNアクセスが有効になっている...
- 質問68 セキュリティ エンジニアは、コンテナー イメージに対して次の要...
- 質問69 セキュリティ アナリストは、Web サーバーで検出された攻撃に関...
- 質問70 エンジニアは、社内電子メール サービスの署名と暗号化のサポー
- 質問71 クラウド ドキュメント リポジトリ内のラベルのないドキュメント...
- 質問72 ある組織のロードバランサーはEOL(サポート終了)に達し、交換が...
- 質問73 システム管理者は、電子メールを介した企業ブランドのなりすまし
- 質問74 マルウェア研究者は、認証情報窃取マルウェアが特定のメモリレジ
- 質問75 マーケティング部門が顧客に送信したメールが、顧客の迷惑メール
- 質問76 顔認識を使用してモバイル デバイスにローカル認証する場合のリ
- 質問77 CI/CD プロセスのセキュリティ レビュー中に、セキュリティ エン...
- 質問78 組織に複数の製品を提供する重要なベンダーがいる場合のリスク評
- 質問79 あるセキュリティアナリストが、ある企業グループのネットワーク
- 質問80 境界ファイアウォール構成を検証するためのベスト プラクティス
- 質問81 脅威ハンターは、APTに関連する潜在的に悪意のあるアクティビテ...
- 質問82 他の暗号化方式と比較した場合の準同型暗号化の利点を最もよく表
- 質問83 複数の国で事業を展開するある企業は、各事業部門ごとにローカル
- 質問84 セキュリティ担当者は、最近のインシデント報告書を確認していた
- 質問85 あるエンジニアは、UNIXサーバー上で毎日コマンドを実行すること...
- 質問86 システム管理者は、企業のクラウドストレージ環境におけるセキュ
- 質問87 セキュリティアナリストは、正当なサードパーティボット関連トラ
- 質問88 最高情報セキュリティ責任者(CIO)は、ランサムウェアによる業...
- 質問89 セキュリティ管理者は、単一のホストからサービスを実行する仮想
- 質問90 組織全体は、暗号化された資料に個別にアクセスできる従業員によ
- 質問91 ある企業は、開発環境で個人情報(PII)データに関するインシデ...
- 質問92 セキュリティアナリストがWebアプリケーションのレビューを行っ...
- 質問93 ベンダー評価において、アナリストは監査レポートに含まれる補完
- 質問94 サイバーセキュリティ インシデントのフォレンジック調査中に、
- 質問95 ある脅威インテリジェンス企業の事業目標は、顧客がAPIを介して...
- 質問96 セキュリティ エンジニアは、従業員が多数の社内サーバーからド
- 質問97 ある組織は、世界中の顧客にバーチャルイベントサービスを提供す
- 質問98 セキュリティエンジニアが会社のメールクラスターに新しいサーバ
- 質問99 セキュリティ エンジニアが ECC を格子ベースの暗号化技術に置き...
- 質問100 モバイル デバイス ハードウェア メーカーは、新しいモバイル プ...
- 質問101 従業員が分散しているグローバル組織のセキュリティ アーキテク
- 質問102 デジタル証拠を法廷に提出するには、証拠は次の条件を満たしてい
- 質問103 インシデント対応チームがマルウェアを分析し、次のことを観察し
- 質問104 最近の報告によると、ソフトウェアツールが悪用されているようで
- 質問105 顧客は、サブスクライブした Web サービスの安全な通信を常に要...
- 質問106 システムエンジニアは、リモートワークのみの従業員向けにSaaSア...
- 質問107 セキュリティ エンジニアは、レガシー アプリケーションに関する...
- 質問108 ある企業は、セキュリティ上のギャップを特定し、潜在的なインシ
- 質問109 ある企業がデータセンターをクラウドに移行しています。一部のホ
- 質問110 ある企業が、スライドテンプレートを使用できる一般的なコラボレ
- 質問111 あるエンジニアは、IEEEが定める802.1Xプロトコルのセキュリティ...
- 質問112 ある組織がインシデント対応計画を策定しました。この計画の有効
- 質問113 クラウド エンジニアは、次のことに対する適切なソリューション
- 質問114 ある企業が、重要なワークロードをデータセンターからクラウドに
- 質問115 ある組織の取締役会は、最高情報セキュリティ責任者(CIO)に対し...
- 質問116 外部の脅威アクターが公共インフラプロバイダーを攻撃しました。
- 質問117 CRM企業は、CSPのPaaSサービスを活用してSaaS製品をホスティング...
- 質問118 ある企業のBIAでは、1時間を超えるデータ損失は事業にとって壊滅...
- 質問119 セキュリティエンジニアは、SIEMプラットフォームから、内部ネッ...
- 質問120 ある組織が最近、異なるEDRソリューションを運用している別の企...
- 質問121 セキュリティ エンジニアが組み込み施設自動化システムのセキュ
- 質問122 一部の従業員がオンラインの個人用ストレージ アカウントにデー
- 質問123 シミュレーション サイト A で、攻撃者がポンプ室の水圧を上昇さ...
- 質問124 運用テクノロジーは、多くの場合、次のような設計前提で作成され
- 質問125 セキュリティチームは、会社の公開ウェブサイトの1つが期待どお
- 質問126 ある企業が最近マルウェアに感染しました。根本原因分析の結果、
- 質問127 セキュリティアーキテクトは、標的型攻撃と思われる攻撃によって
- 質問128 ある企業は、接続文字列の保護を確実にするために、秘密鍵と公開
- 質問129 組織は * 社内外からの問い合わせにタイムリーに対応する * 透明...
- 質問130 ある企業のアプリケーションのセキュリティ監査で、顧客アカウン
- 質問131 ある企業は最近、新しいアプリケーションをサポートするために、
- 質問132 セキュリティエンジニアは、一部のレガシーシステムが依然として
- 質問133 ある企業は、脆弱性を迅速に修正し、本番環境へデプロイするため
- 質問134 ソフトウェアベンダーは、世界中の顧客ベースに定期的な機能追加
- 質問135 ある企業が、データベースに保存されているデータを非表示にする
- 質問136 ある企業が最近、ランサムウェア攻撃に見舞われました。同社はRP...
- 質問137 地元の病院のセキュリティ管理者は、患者の医療記録を安全に保管
- 質問138 ある組織が分散型ワークフォースモデルへの移行を決定しました。
- 質問139 データ流出の申し立てを調査している地方自治体は、悪意のあるユ
- 質問140 セキュリティ アナリストは、セキュリティ インシデントに関連す...
- 質問141 セキュリティエンジニアは、モバイルデバイスのユーザー認証およ
- 質問142 コンプライアンス担当者はビジネスインパクト分析を推進しており
- 質問143 あるグローバル企業は、重要な給与計算業務のアウトソーシング先
- 質問144 ある企業は、OTシステムを社内ネットワークの他の領域から分離し...
- 質問145 ヘルプデスクの技術者が、従業員のノートパソコンがOSを起動でき...
- 質問146 組織は、PKI を実装することで、より強力なセキュリティ対策を確...
- 質問147 ある企業は、社有の電話からモバイル デバイスの BYOD 戦略に移...
- 質問148 セキュリティレビューの結果、クライアントプロキシトラフィック
- 質問149 セキュリティエンジニアは、新ハードウェアの発売に向けてセキュ
- 質問150 セキュリティエンジニアは、開発者エンドポイントとデータ保存用
- 質問151 セキュリティアナリストは、社内ネットワーク内のコンピュータで
- 質問152 セキュリティアナリストは、社内向けウェブブラウザのアップデー
- 質問153 ある組織では、リモート発信者の本人確認のため、コールセンター
- 質問154 A社がB社を買収しました。両社はそれぞれ異なる地理的地域にユー...
- 質問155 ジュニア開発者は、新しいマルウェアがAdvanced RISC Machine(AR...
- 質問156 あるソーシャルメディア企業は、既存の暗号の実装に脆弱性がある
- 質問157 保護された企業データが最近流出しました。SOCはネットワーク侵...
- 質問158 電子メール署名が提供するセキュリティ機能は次のどれですか?
- 質問159 複数のクラウド アプリケーションを使用する企業は、次の点を適
- 質問160 セキュリティ専門家は、新しく導入されたクラウド システムの脆
- 質問161 意思決定の参考となる大量の行動観察データを収集するプロセスを
- 質問162 PQC 実装が重要な理由を最もよく表しているのは次のうちどれです...
- 質問163 ある企業は、サイバーセキュリティ部門のガバナンス構造の成熟度
- 質問164 アプリケーションの使用状況に基づいて、特定の種類のトラフィッ
- 質問165 最高情報セキュリティ責任者(CISO)は、サードパーティのリスク管...
- 質問166 電子メール セキュリティ ソリューションのレビュー中に、セキュ...
- 質問167 セキュリティチームは、営業時間外に、あり得ないアクセスとブル
- 質問168 ネットワーク エンジニアは次のテスト結果を記録しました。 (Exh...
- 質問169 ある組織は、タイポスクワッティングを利用したフィッシングキャ
- 質問170 セキュリティ管理者は3つの異なる証明書を与えられており、それ
- 質問171 ある企業が、所有権を示す印を、識別属性を一切追加することなく
- 質問172 準同型暗号化の一般的な使用例を最もよく表しているのは次のうち
- 質問173 重要文書の漏洩が発生した後、企業は同様のインシデントを将来的
- 質問174 ある企業は、安全でないネットワークを介して文書を転送するため
- 質問175 セキュリティアーキテクトがOIDC実装に関する問題のトラブルシュ...
- 質問176 ある企業は、研究成果を業務に役立てることを目指し、研究能力へ
- 質問177 セキュリティエンジニアは、過去のセキュリティ侵害の事後報告を
- 質問178 ある大学では、自社開発のID管理システムを通じて、全職員と学生...
- 質問179 機密性の高いデータを扱う顧客にサービスを提供する企業は、動的
- 質問180 ある企業は、パートナー企業が取引の合意を拒否するのを防ぎたい
- 質問181 インシデント対応チームは、複数のワークステーションのオフライ
- 質問182 ネットワークへの侵入を企てる試みが、長期間にわたり、少数なが
- 質問183 内部ネットワークへの侵入テストの後、次のレポートが生成されま
- 質問184 世界的なメーカーの主任セキュリティアナリストが、ICSネットワ...
- 質問185 ある報道機関は、忘れられる権利を遵守するために、ユーザーが虚
- 質問186 ある企業は、社内メールの配信にmy-email.comというメールサービ...
- 質問187 セキュリティ アナリストは、EDR ソリューションから次のイベン...
- 質問188 リモート デスクトップ機能が環境に展開された後、さまざまな脆
- 質問189 ある企業が新しいサービス製品を開発しており、セキュリティ責任
- 質問190 ある企業は、社内で開発されたビジネスクリティカルなアプリケー
- 質問191 ある金融サービス組織は、AIを活用して顧客の融資金利決定プロセ...
- 質問192 新たな規制に準拠するため、最高情報セキュリティ責任者(CISO)...
- 質問193 最近の監査で、特定のベンダーがリモート管理できるよう外部に公
- 質問194 セキュリティ アナリストがネットワーク ログを確認すると、次の...
- 質問195 セキュリティエンジニアは、組織の機密データを保護するクラウド
- 質問196 最近、ある医療システムがランサムウェア攻撃に見舞われました。
- 質問197 ある企業は、IoTデバイスを使用して、すべての施設のサーモスタ...
- 質問198 管理者は、社内のモバイルデバイス群をPKIに統合し、デバイスのW...
- 質問199 ユーザーは、企業リソースにアクセスする際にさまざまな問題を経
- 質問200 ある組織は、脅威モデリング機能を含むSOCの構築を目的としたセ...
- 質問201 ある企業は、Webベースのフロントエンドを備えたPaaS(Platform a...
- 質問202 最近のセキュリティ監査により、複数のエンドポイントに次の脆弱
- 質問203 ある企業は、Webベースのアプリケーションをアプリケーション層...
- 質問204 ある企業は、顧客にビデオトレーニングを提供する新しいオンライ
- 質問205 ある政府機関は、国際ローミング中に政府発行のデバイスで携帯電
- 質問206 セキュリティ技術者は、毎晩のバッチ更新によって在庫を追跡する
- 質問207 ある組織は、テンプレートの開発、編集、調査、スケジュール管理
- 質問208 企業は、政府のポリシーに準拠するために制御を実装する際に、次
- 質問209 セキュリティアナリストは、クラウド セキュリティ評価ツールか
- 質問210 ある組織は、同業他社のファイル共有を狙うランサムウェアの増加
- 質問211 セキュリティエンジニアがコードスキャンを実行したところ、多く
- 質問212 あるグローバル企業の最高財務責任者(CFO)が、最高経営責任者...
- 質問213 セキュリティイベントの調査中、アナリストはユーザーが不明な送
- 質問214 ある企業がWindows ServerからLinuxベースのサーバーに移行して...
- 質問215 AI 出力が不正確になる理由を最もよく説明しているのは次のうち...
- 質問216 セキュリティエンジニアは、ゼロトラスト環境におけるエンドユー
- 質問217 最新およびレガシーの金融アプリケーションを混在させたサービス
- 質問218 ある組織は、既存の事業継続対策が、緊急事態発生時に重要な社内
- 質問219 セキュリティ研究者が、ある企業に対し、自社のソリューションの
- 質問220 セキュリティアーキテクトは、以前ウェブアプリケーションのデー
- 質問221 セキュリティ構成では、Linuxシステムへのリモートアクセス接続...
- 質問222 ある企業が、ウェブアプリケーションの新バージョンを本番環境に
