エージェントを含む Microsoft Foundry プロジェクトがあります。
エージェントは、内部コンテンツを取得したり、外部APIを呼び出したりするためにツールを使用します。エージェントは、モデルがツールを呼び出すタイミングを決定するように構成されています。
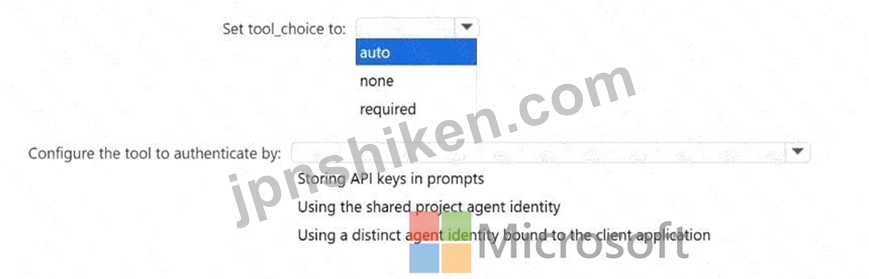
コンプライアンスワークフロー用のエージェントを公開する必要があります。ソリューションは以下の要件を満たす必要があります。
* 各ワークフロー実行には、応答を生成する前に取得ステップを含める必要があります。
* ツール呼び出しは、公開されたエージェント自身のIDを使用して認証を行う必要があります。
* ツールへのアクセスには、他のプロジェクトリソースから隔離されたIDを使用する必要があります。
* ツールへのアクセスは監査追跡をサポートする必要があります。
どうすればよいですか?回答するには、回答欄で適切な選択肢を選んでください。
注:正解ごとに1ポイントが加算されます。
エージェントは、内部コンテンツを取得したり、外部APIを呼び出したりするためにツールを使用します。エージェントは、モデルがツールを呼び出すタイミングを決定するように構成されています。
コンプライアンスワークフロー用のエージェントを公開する必要があります。ソリューションは以下の要件を満たす必要があります。
* 各ワークフロー実行には、応答を生成する前に取得ステップを含める必要があります。
* ツール呼び出しは、公開されたエージェント自身のIDを使用して認証を行う必要があります。
* ツールへのアクセスには、他のプロジェクトリソースから隔離されたIDを使用する必要があります。
* ツールへのアクセスは監査追跡をサポートする必要があります。
どうすればよいですか?回答するには、回答欄で適切な選択肢を選んでください。
注:正解ごとに1ポイントが加算されます。


