- ホーム
- Cisco
- 300-730J - Implementing Secure Solutions with Virtual Private Networks (300-730日本語版)
- Cisco.300-730J.v2026-09-10.q147
- 質問127
有効的な300-730J問題集はJPNTest.com提供され、300-730J試験に合格することに役に立ちます!JPNTest.comは今最新300-730J試験問題集を提供します。JPNTest.com 300-730J試験問題集はもう更新されました。ここで300-730J問題集のテストエンジンを手に入れます。
300-730J問題集最新版のアクセス
「298問、30% ディスカウント、特別な割引コード:JPNshiken」
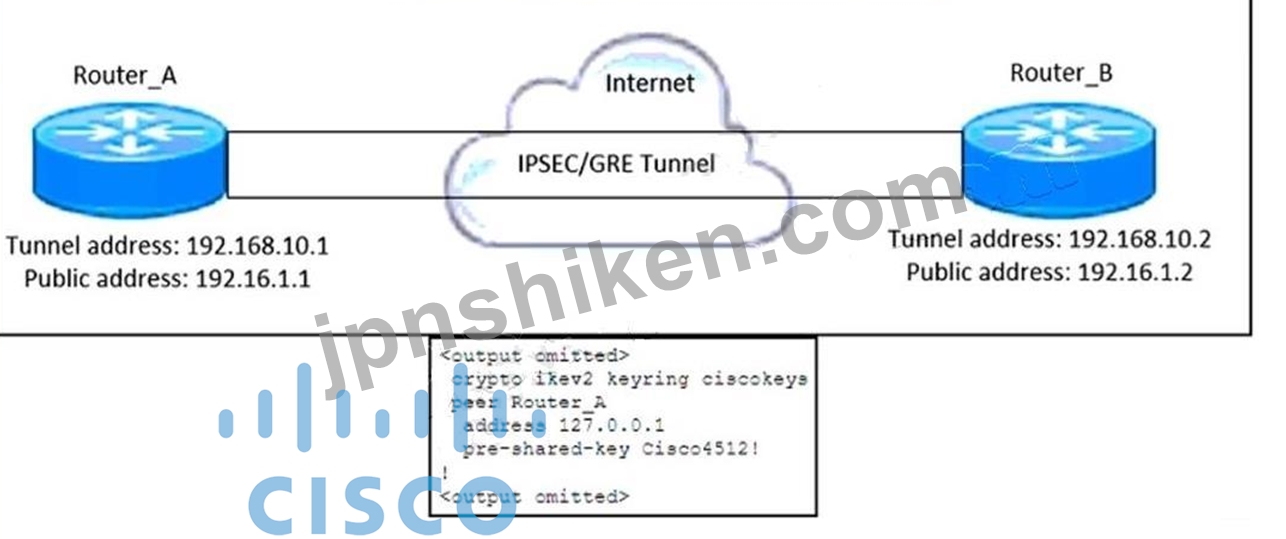
展示を参照してください。エンジニアは、2 台の Cisco ルータ間で iPsec を使用する FlexVPN サイト間 GRE トンネルを設定する必要があります。示された設定は Router_B に適用されましたが、トンネルが起動しません。問題を解決するには、Router_B にどの IP アドレスを設定する必要がありますか。

正解:A
In the provided configuration snippet from Router_B, the IKEv2 keyring is configured with the following peer entry:
crypto ikev2 keyring ciscokeys
peer Router_A
address 127.0.0.1
pre-shared-key Cisco4512!
The issue here is that the address 127.0.0.1 (loopback) is incorrectly set as the peer's address. In a site-to-site FlexVPN with GRE over IPsec, the public IP address of Router_A should be used as the peer address instead.
Router_A's public IP address is 192.16.1.1, so Router_B's configuration should be updated as follows:
crypto ikev2 keyring ciscokeys
peer Router_A
address 192.16.1.1
pre-shared-key Cisco4512!
This change ensures that Router_B correctly identifies Router_A using its real public IP address instead of an invalid loopback address.
crypto ikev2 keyring ciscokeys
peer Router_A
address 127.0.0.1
pre-shared-key Cisco4512!
The issue here is that the address 127.0.0.1 (loopback) is incorrectly set as the peer's address. In a site-to-site FlexVPN with GRE over IPsec, the public IP address of Router_A should be used as the peer address instead.
Router_A's public IP address is 192.16.1.1, so Router_B's configuration should be updated as follows:
crypto ikev2 keyring ciscokeys
peer Router_A
address 192.16.1.1
pre-shared-key Cisco4512!
This change ensures that Router_B correctly identifies Router_A using its real public IP address instead of an invalid loopback address.

- 質問一覧「147問」
- 質問1 FlexVPNトンネルで使用する必要がある構成構成はどれですか。...
- 質問2 展示を参照してください。デバッグ出力に基づいて、どのタイプの
- 質問3 エンジニアは、Cisco Secure Firewall ASA でグループ URL 機能...
- 質問4 IPSec Cisco AnyConnectクライアントがデフォルト設定を使用する...
- 質問5 ユーザは、Cisco AnyConnect VPN を介した音声通話で遅延が発生...
- 質問6 展示を参照してください。展示によると、ユーザーが CCNP Web サ...
- 質問7 図を参照してください。図に示されている show crypto ipsec sa ...
- 質問8 クライアントレス SSL VPN シングル サインオンを構成するための...
- 質問9 ネットワーク エンジニアは、ASA ソフトウェア 9.1 を実行してい...
- 質問10 展示を参照してください。IKEv2 サイト間 VPN トンネルの問題は...
- 質問11 VPN 構成で ECDH が必要な場合、どの Diffie Hellman グループを...
- 質問12 展示を参照してください。エンジニアは、2 台の Cisco ルータ間...
- 質問13 EIGRPが設定されている場合に、DMVPNフェーズ2からフェーズ3に移...
- 質問14 展示を参照してください。お客様は、XML プロファイルを使用せず...
- 質問15 管理者は、今後の Cisco AnyConnect 展開にどの認証プロトコルを...
- 質問16 ネットワーク エンジニアは、2 つの Cisco IOS ルータ間に FlexV...
- 質問17 ユーザーがWebVPNポータルページにログインしたときにスマートト...
- 質問18 Cisco ASA の IPsec の場合、セキュリティ アソシエーション ペ...
- 質問19 新しくインストールされた Cisco ASA 上に、10 人の従業員向けに...
- 質問20 IKEv2のどの機能が、VPNヘッドエンドを大量の半オープンなセキュ...
- 質問21 ネットワーク管理者は、https://www.badsite.com の既知のマルウ...
- 質問22 企業の遠隔地は、MPLS を介してデータセンターに接続します。新...
- 質問23 FlexVPNのどの利点がIKEv1を使用するDMVPNの制限ですか?...
- 質問24 FlexVPN を構成する場合、IKEv2 用に構成する必要がある 2 つの...
- 質問25 エンジニアは Cisco IOS ルータに FlexVPN ソリューションを実装...
- 質問26 図を参照してください。エンジニアがCisco Adaptive Security Ap...
- 質問27 ネットワーク管理者は、内部の Microsoft Active Directory サー...
- 質問28 ネットワーク管理者が Cisco ASA に IKEv2 Cisco AnyConnect を...
- 質問29 ECDHとECDSAの2つの機能は何ですか? (2つ選択してください。)...
- 質問30 展示を参照してください。新しい IPsec VPN トンネルが設定され...
- 質問31 エンジニアが、IOS XEを実行しているCiscoルータ上で、事前共有...
- 質問32 Cisco AnyConnectクライアントにヘッドエンドの復元力を提供する...
- 質問33 ネットワーク管理者が Cisco ASA 上で WebVPN を実装しており、...
- 質問34 ユーザがブックマーク リストを使用して接続プロファイルを設定
- 質問35 展示を参照してください。スポークと 2 つの DMVPN ハブ間の VPN...
- 質問36 エンジニアは、2 つの Cisco ASA がクライアントレス SSLVPN ア...
- 質問37 GETVPN、FlexVPN、DMVPN ではどれが使用されていますか?...
- 質問38 Cisco ASAクライアントレスSSL VPNソリューションについて正しい...
- 質問39 ASAのVPNロードバランシングはどのVPNをサポートしていますか?...
- 質問40 show crypto isakmp sa コマンドを実行したときに、IKEv1 フェー...
- 質問41 Cisco AnyConnectクライアントは、本社のASAとのSSL VPN接続を確...
- 質問42 企業は、企業が発行したラップトップおよびデバイスのみが Cisco...
- 質問43 ドラッグアンドドロップの質問 GETVPN コンポーネントを左側から...
- 質問44 ドラッグアンドドロップの質問 右側の正しいコマンドを左側のコ
- 質問45 トンネルグループリストを使用せずにVPNセッションをトンネルグ...
- 質問46 ASAが非標準のアプリケーションとWebリソースを処理して、クライ...
- 質問47 FlexVPN で使用するのに推奨される暗号化技術はどれですか? (2 ...
- 質問48 Cisco IOS ルータは、別の DMVPN フェーズ 3 クラウドの一部であ...
- 質問49 エンジニアは、次の要件を満たすリモート アクセス VPN ソリュー...
- 質問50 展示を参照してください。どのタイプの VPN が使用されています...
- 質問51 組織は、25,000 の同時ユーザーをサポートする 12 の VPN ヘッド...
- 質問52 ユーザがクライアントレス SSLVPN 機能を使用して Cisco ASA に...
- 質問53 スマートトンネルが適切に機能するための要件は何ですか?
- 質問54 ドラッグアンドドロップの質問 Cisco ASA でクライアントレス SS...
- 質問55 展示を参照してください。グループ Cisc012345678 にはどのタイ...
- 質問56 GETVPNについて正しい説明はどれですか。
- 質問57 管理者は、リモートユーザー向けにクライアントレスVPNソリュー...
- 質問58 どのコマンドで、DMVPNスポークがトンネルとNBMAのマッピングを...
- 質問59 IPsec トンネルからのパケットとペイロードがファイアウォール上...
- 質問60 図を参照してください。DMVPN フェーズ 2 構成からどのような 2 ...
- 質問61 Cisco AnyConnectは、TLSセッション確立後、レイテンシに敏感な...
- 質問62 ある組織は、すべてのサイト間の直接通信で 350 のサイトをサポ...
- 質問63 展示を参照してください。show run コマンドの出力に基づいて、...
- 質問64 ライセンスに関して、適応型セキュリティ アプライアンスで IKEv...
- 質問65 特定の内部サブネット内のデバイスがポート 443 を使用してのみ...
- 質問66 ドラッグアンドドロップの質問 左側の GET VPN コンポーネントを...
- 質問67 図を参照してください。エンジニアがCisco ASA上でクライアント...
- 質問68 展示を参照してください。2 つのサイト間にトンネルを設定すると...
- 質問69 IPsec VPN トンネル構成でオプションのパラメーターはどれですか...
- 質問70 スポークツースポークトンネルが許可されていないFlexVPNハブア...
- 質問71 クライアントレスSSL VPN構成におけるWebタイプのアクセス制御リ...
- 質問72 1 日に何千もの固有の Cisco AnyConnect 接続がある環境で、2 つ...
- 質問73 ユーザは、クライアントレス SSLVPN を使用して Cisco ASA にロ...
- 質問74 展示を参照してください。ユーザーは AnyConnect SSLVPN 経由で...
- 質問75 ネットワーク エンジニアが、Cisco ASA でクライアントレス SSLV...
- 質問76 GETVPN を使用して企業オフィス間のネットワークを横断する利点...
- 質問77 FlexVPN用に設定されたルーター間でルーティング情報が交換され...
- 質問78 管理者は、数人のユーザーに対して初めて AnyConnect を設定して...
- 質問79 DMVPN スポークが他の DMVPN スポークへのルートを学習するには...
- 質問80 展示を参照してください。顧客は 2 つの Cisco ASA デバイス間で...
- 質問81 ネットワーク管理者は、www.cisco.com へのすべてのトラフィック...
- 質問82 展示を参照してください。DMVPN スポークツースポーク トラフィ...
- 質問83 展示を参照してください。プライマリ プロトコルとして IPsec を...
- 質問84 Cisco ASA でクライアントレス VPN を実装するには、どの 2 つの...
- 質問85 ドラッグアンドドロップ問題 エンジニアがASDMを使用して、Cisco...
- 質問86 プライベート WAN でマルチキャスト トラフィックを暗号化すると...
- 質問87 ネットワーク エンジニアがサーバーを構成しています。ルーター
- 質問88 展示を参照してください。Cisco ASA は、FlexVPN サーバーとして...
- 質問89 サイト間VPNを介してマルチキャストトラフィックを送信するため...
- 質問90 リモートトンネルエンドポイントのネットワークルートを動的にイ
- 質問91 DMVPN フェーズ 3 の実装に固有の 2 つの NHRP 機能はどれですか...
- 質問92 ある企業は、支社からの接続を受け入れるために、本社の Cisco A...
- 質問93 展示を参照してください。ユーザーは、プライベート IP アドレス...
- 質問94 展示を参照してください。ネットワーク エンジニアが Cisco IOS ...
- 質問95 展示を参照してください。ネットワーク エンジニアがメンテナン
- 質問96 キーサーバーのグループからプライマリキーサーバーを選択するた
- 質問97 Cisco IOS GETVPN キー サーバ構成で必要な 2 つのコンポーネン...
- 質問98 VPNヘッドエンドでIKEv2フラグメンテーションを有効にすることで...
- 質問99 ネットワーク エンジニアは、請負業者が内部サーバーにアクセス
- 質問100 展示を参照してください。IPsec Cisco AnyConnect クライアント...
- 質問101 ある企業は、ユーザーVPNアクセス用のソリューションを必要とし...
- 質問102 http-only-cookie コマンドが有効な場合に動作するクライアント...
- 質問103 展示を参照してください。VPN トンネル経由でアクセスできるはず...
- 質問104 Cisco ASAはアクティブ/スタンバイモードで設定されています。 C...
- 質問105 展示を参照してください。ネットワーク管理者は、Cisco AnyConne...
- 質問106 ssl トラストポイント <トラストポイント名> で使用されて...
- 質問107 エンジニアは、トンネルの確立後にプライマリ FlexVPN サーバー...
- 質問108 AnyConnectクライアントとFlexVPSヘッドエンドを使用する場合、...
- 質問109 展示を参照してください。GETVPN 展開が適切に機能するためには...
- 質問110 ネットワーク管理者は Cisco IPS アプライアンスを導入しており...
- 質問111 SSLをサポートするリモートアクセスVPNソリューションはどれです...
- 質問112 フェイルオーバー冗長性のために FlexVPN 上で機能する 2 つの動...
- 質問113 GETVPN の特徴は次のうちどれですか? (2 つ選択してください。)...
- 質問114 Cisco AnyConnectクライアントは、VPNセッションを介して大きな...
- 質問115 ネットワーク管理者は、内部の Microsoft Active Directory サー...
- 質問116 展示を参照してください。どのタイプの VPN 実装が表示されてい...
- 質問117 企業ネットワーク セキュリティ ポリシーでは、すべてのインター...
- 質問118 ネットワーク エンジニアは、会社のラップトップに Cisco AnyCon...
- 質問119 ハブからダイナミック IP アドレスを受信するには、FlexVPN スポ...
- 質問120 Cisco ASAのリモートアクセスVPNにおける動的アクセスポリシーの...
- 質問121 ネットワーク エンジニアは、SSL VPN を構成して、リモート ユー...
- 質問122 DMVPNハブのどのコマンドを使用すると、スポークが登録される際...
- 質問123 Cisco GETVPN環境において、重要なサーバー冗長性を提供する機能...
- 質問124 エンジニアは、次の基準に従って VPN ソリューションを設計する...
- 質問125 変換セットを明示的に定義する必要があるリモート アクセス VPN ...
- 質問126 FlexVPNハブでは、接続する各スポークごとに個別の仮想アクセス...
- 質問127 展示を参照してください。エンジニアは、2 台の Cisco ルータ間...
- 質問128 DMVPN のトラブルシューティング時にピアで BFD が欠落している...
- 質問129 ECC と RSA の 2 つの違いは何ですか? (2つ選んでください。)...
- 質問130 図を参照してください。DMVPN スポークはハブとのセッションを確...
- 質問131 ネットワーク セキュリティ管理者がサイト間 IPsec VPN ピアを構...
- 質問132 トラブルシューティング中に、エンジニアは show crypto isakmp ...
- 質問133 Cisco ASA 上の Secure Client リモート アクセス VPN のトンネ...
- 質問134 Cisco GETVPN環境において、グループメンバーがキーサーバーに登...
- 質問135 展示を参照してください。ネットワーク セキュリティ管理者は、2...
- 質問136 展示を参照してください。ユーザーが内部サーバー 192.168.0.10 ...
- 質問137 クライアントレス SSLVPN を ASA に実装するときに、ネットワー...
- 質問138 あるエンジニアが顧客向けにDMVPNトポロジーを設計しています。...
- 質問139 動的に割り当てられたパブリック IP アドレスを使用してスポーク...
- 質問140 管理者は、リモートアクセスVPNを構成して、企業ネットワーク10....
- 質問141 クライアントレスSSL VPN構成におけるWebタイプのアクセス制御リ...
- 質問142 ルーターがハブを介してトラフィックを送信するのではなく、動的
- 質問143 図を参照してください。エンジニアがDMVPNを使用する環境でブラ...
- 質問144 エンジニアは IPsec VPN を構成しており、信頼性が高く、ACK と...
- 質問145 エンジニアは、2 つのサイト間にフェーズ 1 およびフェーズ 2 ト...
- 質問146 IOS FlexVPN クライアントの有効なバックアップ オプションはど...
- 質問147 管理者は、内部 RDP サーバにアクセスする必要があるユーザのた...
